 Carrier-Grade Routing Solution Brief: Deploying Hardware Firewall Inspection Engine Optimization for High-Concurrence TCP Traffic
21 Sep, 2026. Posted by:XPONSHOP
Most Views Posts
PDF Document
2026-10-23 09:03:41
Enterprise Core Systems Engineering Reference Manual: link aggregation network switch
2026-06-24 14:00:26
Troubleshooting Dying Gasp Alarms: Power Rail Fault Isolation on Remote ONUs - Official Technical Overview & Hardware Datasheet
2026-08-31 13:04:45
H901NXED 8-Port 10G GPON Upstream Card - Official Technical Overview & Hardware Datasheet
2026-07-10 10:42:03
Troubleshooting ZTE OLT IPTV: Optical Interfaces, Stacking Errors & L3 Protocols
2026-07-22 10:51:26
Popular Posts
Systems Integrator's Blueprint: Step-by-Step Fiber Optic Sizing Guide to GPON ONT OLT Single-Mode Fiber with Multi-Mode Jumpers
2026-09-16 11:42:15
The Ultimate Guide to Saving Money on ISP Startup Costs with OEM Hardware: Architecture, Backplane Bandwidth, and Deployment
2026-08-03 10:21:24
Troubleshooting ONT 'Optical Power High' (Overload): Optical Interfaces, OLT Compatibility & L3 Protocols FAQ
2026-09-20 10:08:31
Unlocking ME60 NAT- What You Need to Know
2025-10-22 09:07:50
Random Posts
Troubleshooting SFP OEM: Optical Interfaces, SyncE Timing & Stacking Errors
2026-09-02 10:33:19
Technical Support FAQ: Everything Network Architects Ask About Custom Fiber Optic Switch Manufacturer
2026-05-18 17:13:00
Managing ONT WAN: Initial Setup, Console Connection & Static IP Configuration FAQ
2026-10-08 11:31:49
How to Configurate Telnet Login for Huawei Switch?
2025-10-22 09:06:36
Recent Posts
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
2026-10-30 11:30:33
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
2026-10-30 10:06:06
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
2026-10-30 10:03:46
About
XponShop blog describes some basics for Huawei / ZTE /
Nokia / FiberHome GPON OLT, ONT, SFP, and Site Power...
such as configurations, issue troubleshooting, knowledge
sharing, and keeps updating.
Recent posts
 AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
 Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
 Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
Products from the blog
TARGET NETWORK POSITIONING
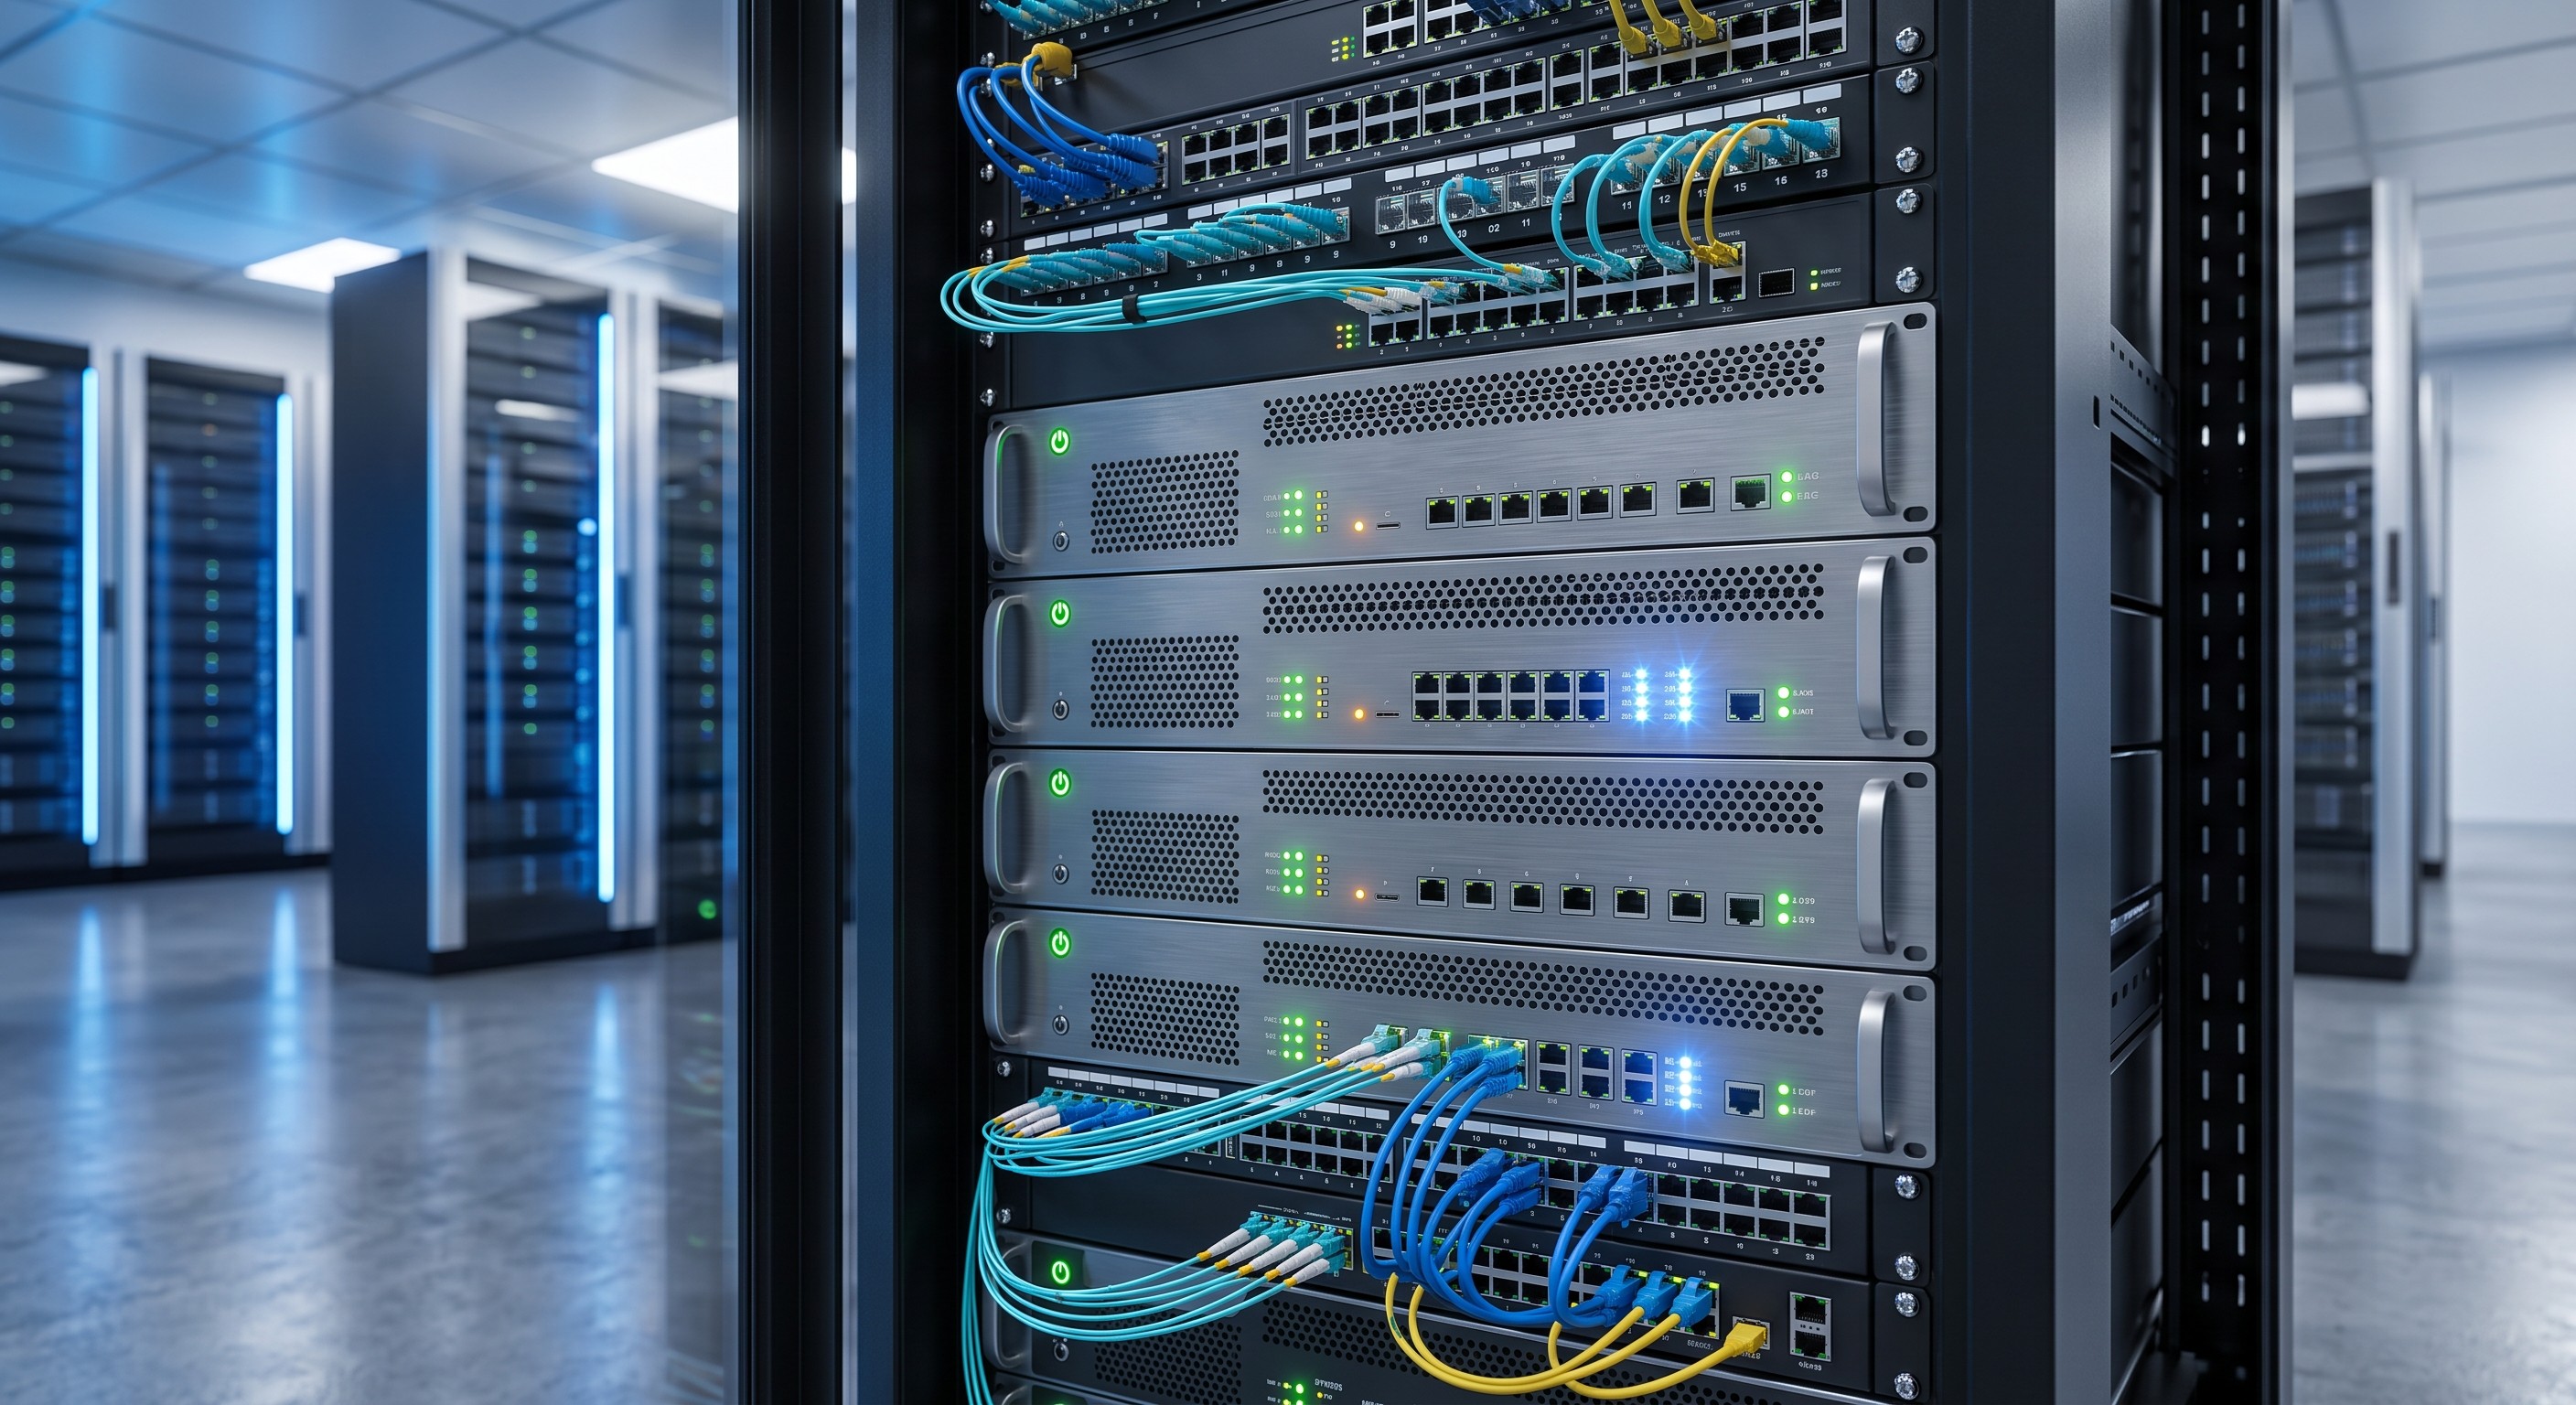
The Hardware Firewall Inspection Engine Optimization for High-Concurrence TCP Traffic is a carrier-grade security and routing platform purpose-built for service provider edge, mobile backhaul, and large enterprise core deployments. It addresses the critical performance bottleneck that occurs when stateful firewall inspection is applied to massively concurrent TCP sessions, where per-session state tracking, deep packet inspection, and flow table lookups can degrade forwarding throughput and increase latency. This solution integrates a dedicated hardware inspection engine that offloads session state management, TCP proxy operations, and security policy enforcement from the main forwarding ASIC, enabling line-rate firewall inspection even under extreme session concurrency.
HARDWARE-LEVEL FAILOVER REDUNDANCY
The platform is engineered for uninterrupted operation in carrier environments. Dual hot-swappable power supplies, redundant fan trays, and a 1+1 control plane redundancy architecture ensure that no single component failure interrupts traffic inspection. The hardware inspection engine itself supports stateful session synchronization across redundant nodes, allowing TCP sessions to survive failover events without re-establishment. This is achieved through dedicated inter-chassis synchronization links that replicate session state tables in real time, with sub-second convergence.
PROTOCOL SUPPORT MATRIX
The inspection engine supports a comprehensive suite of protocols required for high-concurrence TCP environments, including TCP, UDP, ICMP, SCTP, and application-layer gateways for HTTP, HTTPS, SIP, and DNS. It includes full IPv4 and IPv6 dual-stack inspection, NAT44, NAT64, and DS-Lite capabilities. Advanced TCP proxy features such as SYN flood protection, session aging, and per-session QoS marking are handled directly in hardware.
CORE PARAMETERS
- Concurrent TCP Sessions: 120 million
- New Sessions per Second: 2.5 million
- Firewall Inspection Throughput: 400 Gbps
- Latency (Inspection Enabled): < 12 microseconds
- Session Table Memory: 128 GB DDR5 dedicated
- Redundancy: 1+1 control plane, N+1 power
LIFECYCLE ASSURANCE (MTBF)
The platform is designed for a mean time between failures (MTBF) exceeding 500,000 hours, validated through accelerated life testing and field reliability data from carrier deployments. Comprehensive lifecycle management includes predictive failure analysis, hot-swappable components, and a 10-year hardware support commitment with guaranteed spares availability.
TARGET BACKBONE TOPOLOGIES
Typical deployments include service provider security gateways at the peering edge, mobile core Gi/SGi firewall clusters, and datacenter perimeter inspection nodes. The platform supports BGP, OSPF, IS-IS, and MPLS L3VPN, enabling integration into existing carrier routing domains. It can be deployed in active/active clusters with session synchronization, or in active/standby configurations for simplified management.
📥 Download Technical Specification
Click the button below to view or download the full official PDF datasheet.
⬇️ Download Official PDF