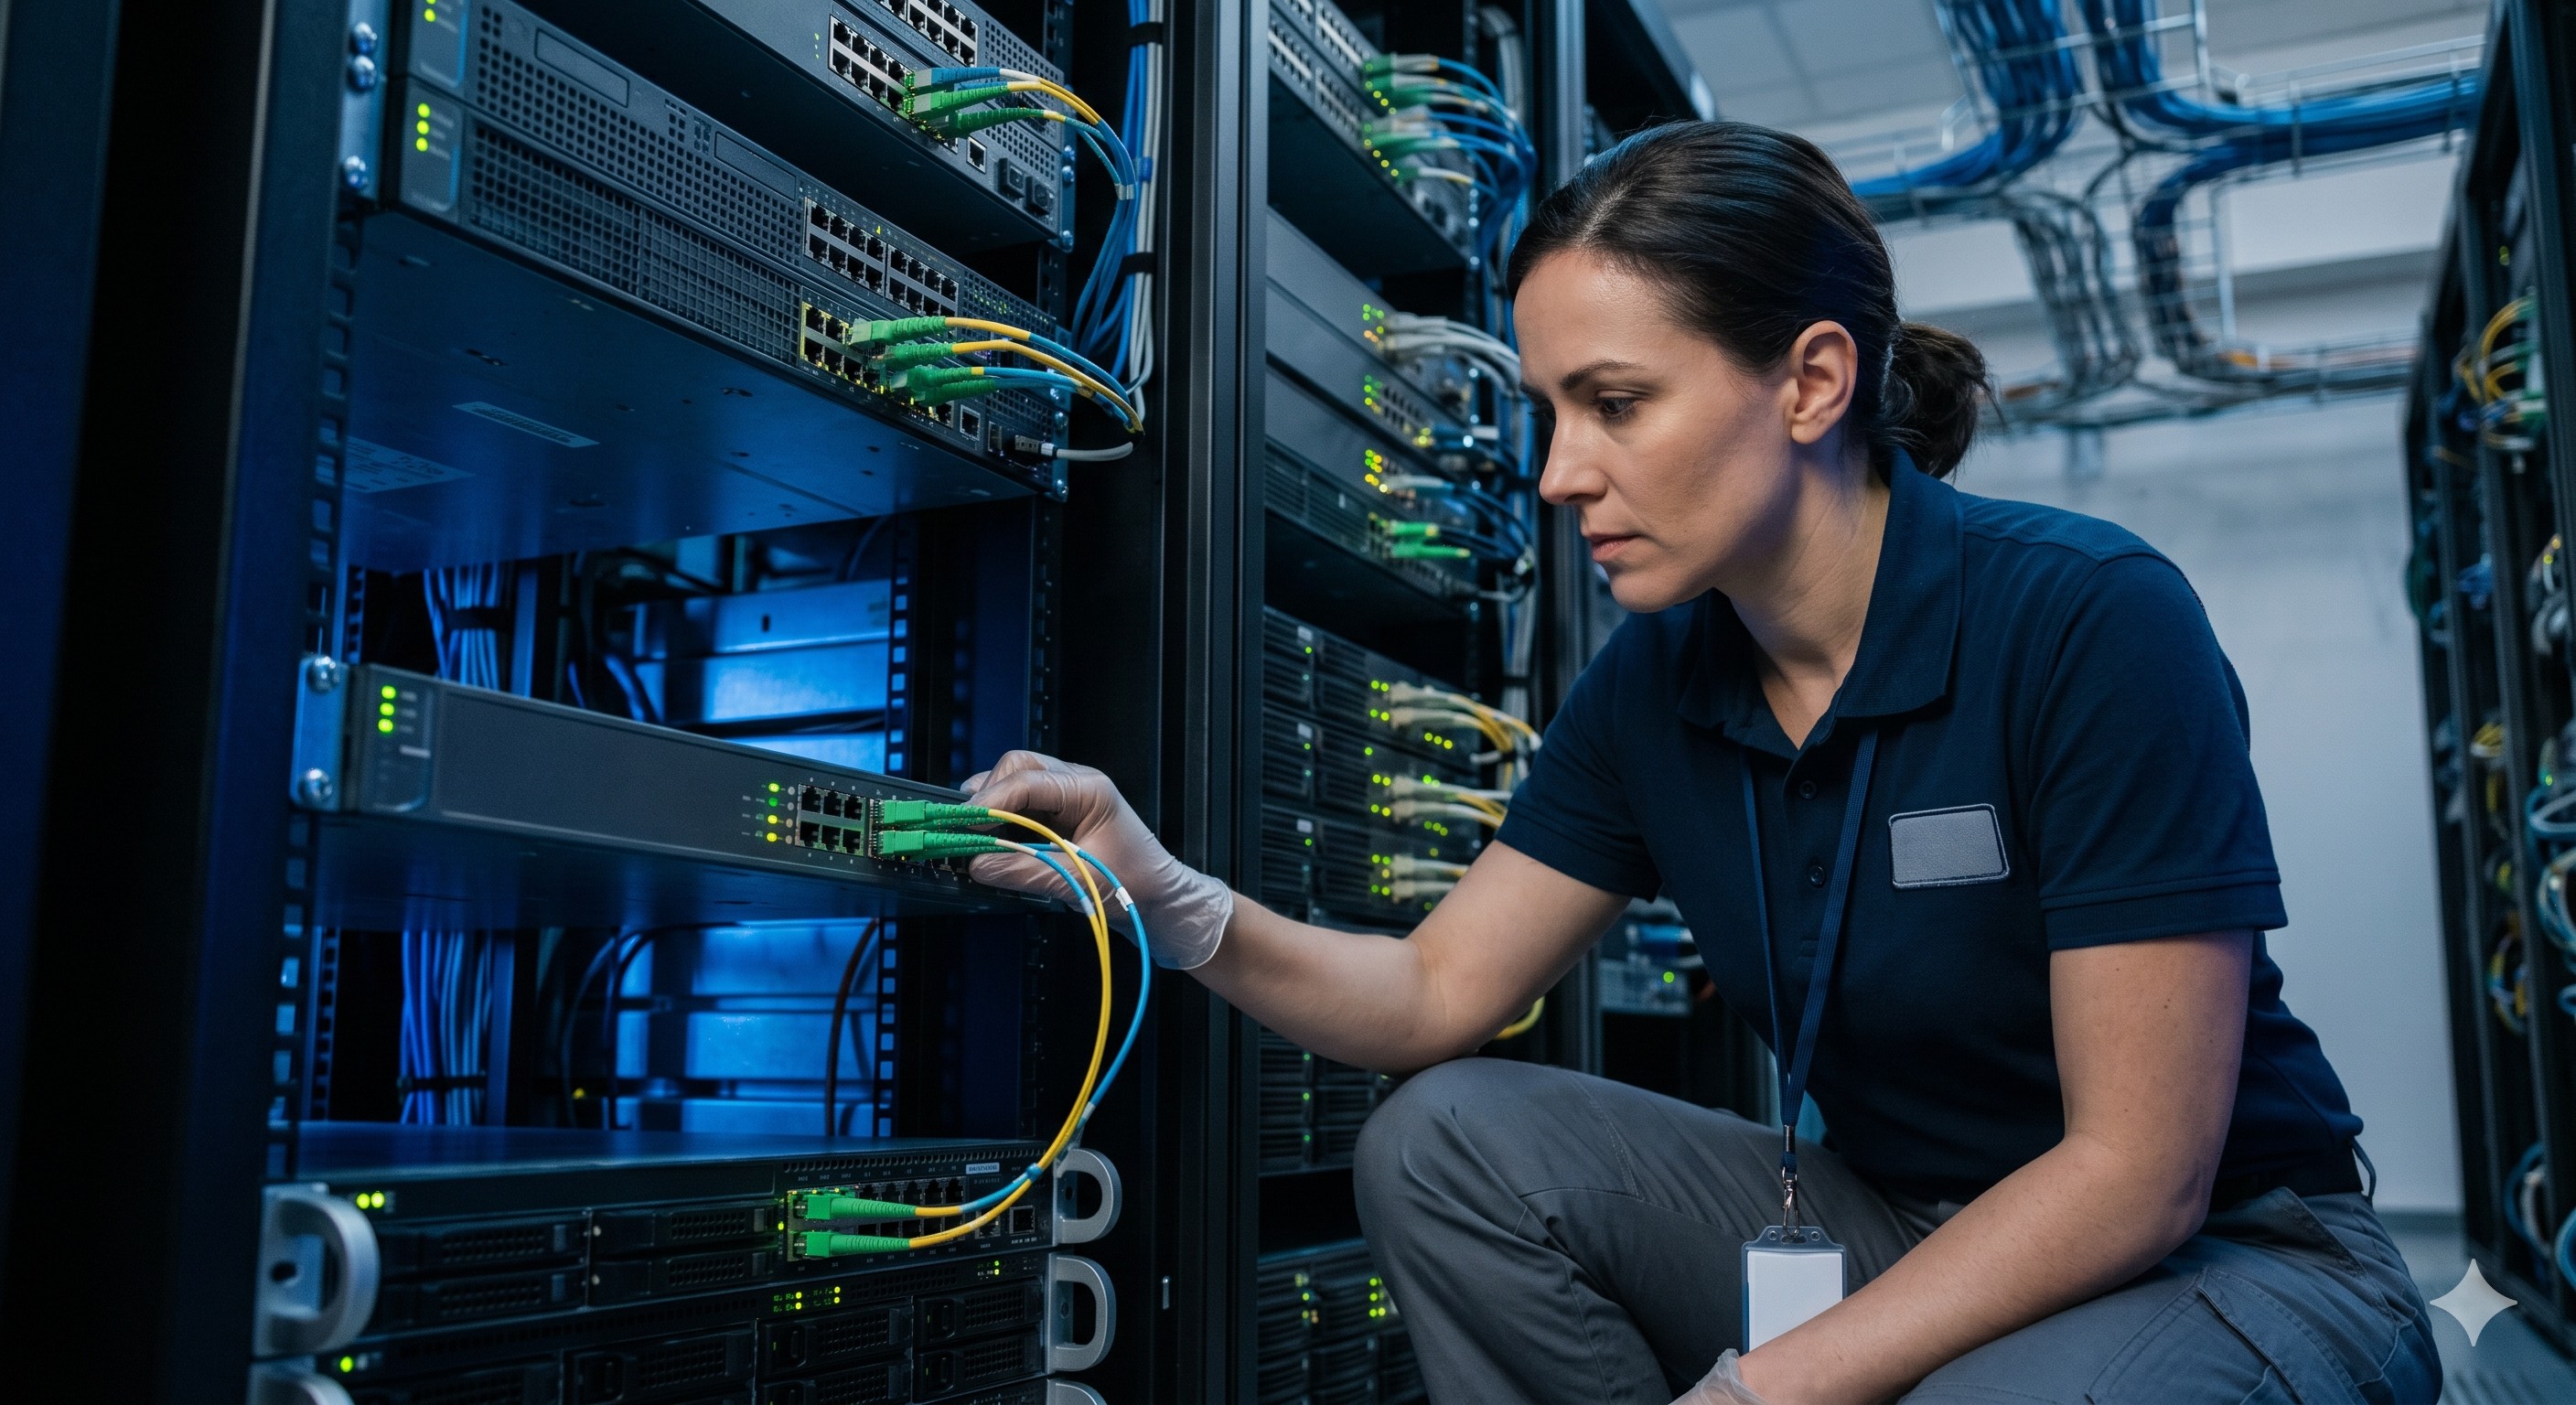
 Deploying server virtualization high density network interface in Datacenters: 8 Critical Layer 3 Routing Questions
16 Jun, 2026. Posted by:XPONSHOP
Most Views Posts
What is SNMP in Network Switch FAQ: Expert Answers to Network Integration & Configuration Questions
2026-06-24 13:38:20
QoS Priority Queuing CoS DSCP FAQ: Expert Answers to Network Integration & Configuration Questions
2026-05-29 15:55:25
High-Density Datacenter Scaling: Integrating Dirty Optical Bulkhead Connectors at the Aggregation Layer
2026-09-18 09:21:42
Popular Posts
Overcoming Network Bottlenecks: Enterprise Configuration Manual for IGMP Fast Leave IPTV Channel Switching
2026-10-09 09:31:43
Troubleshoot Frequent ONU Offline on ZTE ZXA10 Cxx OLT
2025-12-22 16:22:33
Troubleshooting ONT: Optical Interfaces, Stacking Errors & L3 Protocols
2026-09-08 10:37:33
Strategic Enterprise Asset Procurement Evaluation Report: Enterprise Router Factory Reset Protocol
2026-06-10 14:01:18
Troubleshooting 100Mbps ONT: Optical Interfaces, Stacking Errors & L3 Protocols
2026-09-07 10:13:25
Random Posts
OEM Dynamic Bandwidth Allocation (DBA) T-CONT Registry Mapping on ZTE OLT Platforms - Official Technical Overview & Hardware Datasheet
2026-08-04 09:48:15
Troubleshooting GPON: Optical Interfaces, Stacking Errors & L3 Protocols
2026-06-30 13:57:55
Carrier Ethernet Technical Standard Compliance Register: CE 2.0 E-Line and E-LAN Provisioning Standards
2026-09-29 09:25:19
Recent Posts
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
2026-10-30 11:30:33
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
2026-10-30 10:06:06
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
2026-10-30 10:03:46
About
XponShop blog describes some basics for Huawei / ZTE /
Nokia / FiberHome GPON OLT, ONT, SFP, and Site Power...
such as configurations, issue troubleshooting, knowledge
sharing, and keeps updating.
Recent posts
 AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
 Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
 Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
Products from the blog
Overview
For network architects and infrastructure engineers, deploying a server virtualization high density network interface is a critical step in modernizing the data center backbone. This FAQ addresses the most complex technical challenges, from optical interoperability to ensuring high availability in dense virtualized environments, providing authoritative answers for both pre-sales planning and post-sales troubleshooting.
Frequently Asked Questions