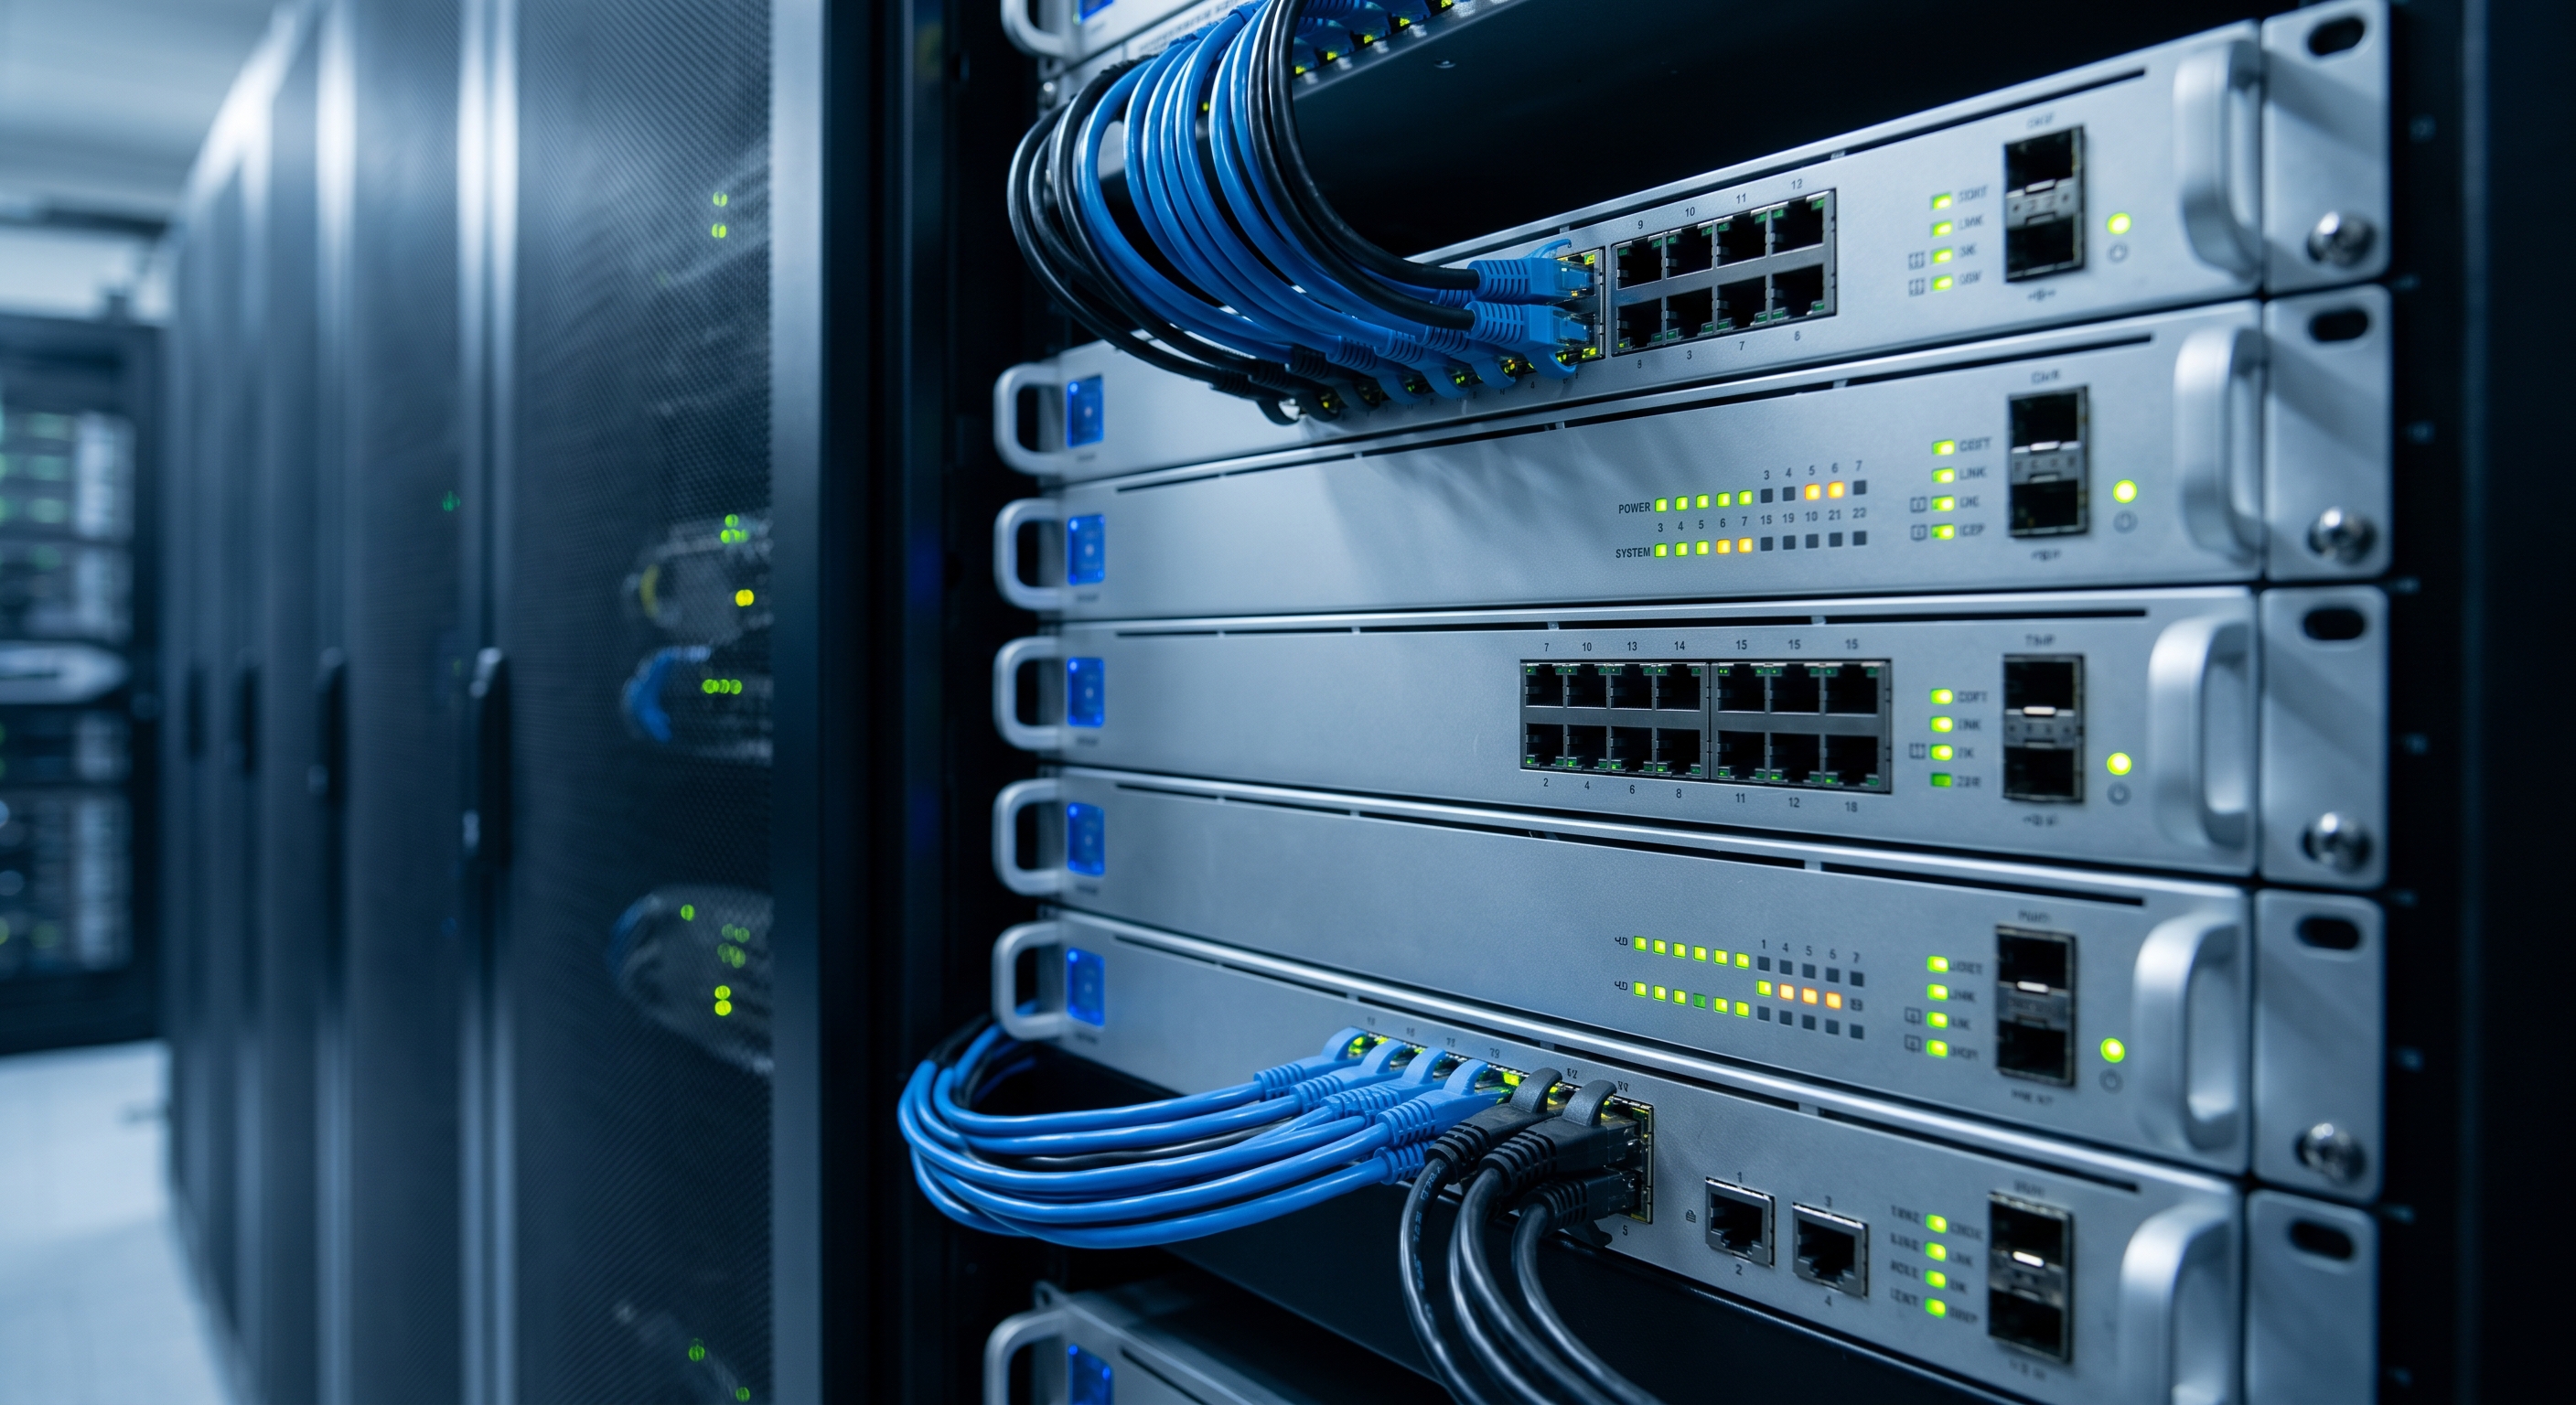
 High-Performance Alternative Fixed Configuration Firewall Session Limits - Official Technical Overview & Hardware Datasheet
07 Sep, 2026. Posted by:XPONSHOP
Most Views Posts
Carrier Ethernet Technical Standard Compliance Register: Industrial Ethernet Switch Ring Topology Recovery Protocols (ERPS G.8032)
2026-09-24 09:40:47
High-Density Fiber Infrastructure Application Note: XPONSHOP Cost-Effective Alternative Fiber Cross-Connect Cabinet Splicing Guide
2026-07-30 10:44:44
Troubleshooting {keyword}: Optical Interfaces, Stacking Errors & L3 Protocols
2026-09-11 08:25:59
Popular Posts
Huawei OptiXstar B651G-X - Official Technical Overview & Hardware Datasheet
2026-07-16 14:19:08
XPON ONU Compatibility FAQ: Expert Answers to Network Integration & Configuration Questions
2026-07-03 10:46:39
Systems Integrator's Blueprint: Step-by-Step Fiber Optic Sizing Guide to ONT Pre-Configuration for Rapid Field Deployment
2026-09-08 10:52:35
Troubleshooting ONU Optical Power: CLI Diagnosis, Thresholds & Alarms
2026-07-06 14:05:04
Random Posts
Troubleshooting Huawei & ZTE ONT: Optical Interfaces, Wi-Fi Errors & L3 Protocols
2026-09-03 10:13:44
Troubleshooting What causes intermittent packet loss when running a ping test from an ONT?: Optical Interfaces, Stacking Errors & L3 Protocols
2026-09-16 11:44:05
Switch MAC Address Table Exhaustion Countermeasures and Port Security Profiles - Official Technical Overview & Hardware Datasheet
2026-09-29 09:31:53
Recent Posts
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
2026-10-30 11:30:33
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
2026-10-30 10:06:06
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
2026-10-30 10:03:46
About
XponShop blog describes some basics for Huawei / ZTE /
Nokia / FiberHome GPON OLT, ONT, SFP, and Site Power...
such as configurations, issue troubleshooting, knowledge
sharing, and keeps updating.
Recent posts
 AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
 Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
 Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
Products from the blog
PRODUCT IDENTIFICATION
Product Designation: High-Performance Alternative Fixed Configuration Firewall Session Limits Platform
Product Series Identifier: FS-7000 Series
Target Market: Enterprise Edge, Campus Gateway, and Carrier-Grade Perimeter Security
Compliance Classification: Fixed-Form-Factor High-Density Firewall Appliance
CORE INTERNAL TOPOLOGY
The FS-7000 Series leverages a purpose-built, non-blocking internal architecture engineered to enforce stateful firewall policies at wire speed without compromising session table integrity. At the heart of the system resides a dedicated session management ASIC that maintains a concurrent session table exceeding 10 million entries, a critical metric for high-density subscriber aggregation and data center interconnection.
The internal data bus comprises a dual-redundant 400 Gbps fabric interconnect, ensuring sub-50-microsecond inter-processor communication for session synchronization across multiple security contexts. The forwarding plane is decoupled from the control plane, with a dedicated 2.5 GHz multi-core CPU complex managing routing protocols, policy updates, and security intelligence while the ASIC handles packet classification, stateful inspection, and NAT traversal.
SWITCHING SUBSYSTEM CAPABILITIES
The platform implements a full mesh of 10G/25G/40G/100G interfaces, configurable for either WAN-facing throughput or high-density internal segmentation. The switching subsystem operates in cut-through mode for latency-sensitive applications, reducing jitter for voice-over-IP and financial trading workloads, while dynamically reverting to store-and-forward for error-checking of encrypted payloads.
Key packet processing capabilities include:
- Concurrent Session Limit: 10,000,000 active sessions (standard license) / 16,000,000 (performance license)
- New Session Establishment Rate: 1,500,000 CPS (connections per second)
- Hardware-Accelerated IPSec VPN: 40 Gbps throughput (AES-256-GCM)
- Application-Aware Traffic Shaping: supported over 3,000 pre-defined signatures
- Virtual Routing and Forwarding (VRF) Instances: 512 concurrent contexts
OPERATIONAL ADVANTAGES
The High-Performance Alternative Fixed Configuration Firewall offers a compelling value proposition for organizations seeking a tier-1 security posture without the premium associated with proprietary modular chassis systems. The fixed configuration approach reduces mechanical point-of-failure risks, enables rapid deployment, and ensures predictable power and cooling requirements.
Advanced session limit capabilities are leveraged for lawful interception logging, deep packet inspection buffering, and real-time threat intel correlation. The hardware includes redundant solid-state storage for boot and log retention, as well as dual hot-swappable AC/DC power supplies providing N+1 redundancy. The active-active session state synchronization permits zero-downtime upgrades and seamless failover in active/active HA clusters.
The platform has been validated against the most stringent carrier-grade SLA requirements, demonstrating less than 1 microsecond of forwarding jitter under full session load. Telemetry data is exported via gRPC and NETCONF for integration with third-party network management solutions.
SPECIFICATION MATRIX
Firewall Policies and Zones:
- Maximum Security Zones: 256
- Concurrent Policy Rules: 50,000
- Interface Pairs for Stateful Inspection: Unlimited (hardware limited)
- Policy-Based Routing: Supported across 1,024 routing instances
Network Layer Support:
- IPv4 and IPv6 dual-stack stateful inspection
- Multicast forwarding (IGMP v2/v3, MLD)
- GRE, VXLAN, and MPLS-over-GRE tunneling
- Integrated DHCP Server/Relay and DNS Forwarder
Management and Programmability:
- CLI (SSHv2) with hierarchical command structure
- Web-based GUI with role-based access control (RBAC)
- RESTCONF and NETCONF (RFC 6241 compliant)
- SNMP v2c/v3, syslog, and sFlow monitoring
- Zero-Touch Provisioning (ZTP) via DHCP options and cloud orchestration
REGULATORY COMPLIANCE
The FS-7000 Series has undergone extensive testing and certification to meet the following regulatory and industry standards, making it suitable for deployment in global telecommunications, financial, and government networks.
- Safety: UL 60950-1 / UL 62368-1, EN 60950-1, EN 62368-1, CB Scheme, IEC 60950-1/62368-1
- EMC: FCC Part 15 Subpart B (Class A), EN 55032 Class A, EN 55024, CISPR 32, VCCI (Class A), AS/NZS CISPR 32
- Environmental: RoHS Directive 2011/65/EU, WEEE 2012/19/EU, REACH (SVHC compliance)
- Telecom: NEBS Level 3 (GR-63-CORE / GR-1089-CORE) – certified upon request
- Cybersecurity: FIPS 140-2 Level 2 (hardware root of trust), Common Criteria EAL-4+ (NIST SP 800-131A compliant cryptographic algorithms)
📥 Download Technical Specification
Click the button below to view or download the full official PDF datasheet.
⬇️ Download Official PDF