 Secured Routing Platform - Official Technical Overview & Hardware Datasheet
22 Jun, 2026. Posted by:XPONSHOP
Most Views Posts
High-Quality Alternate Cisco-Compatible Consolidation Console Cable Layout Schema - Official Technical Overview & Hardware Datasheet
2026-09-04 09:41:28
Troubleshooting ruggedized ethernet switch cost: Optical Interfaces, Stacking Errors & L3 Protocols
2026-05-22 15:42:13
Troubleshooting 4K IPTV Stream Stuttering on 100Mbps ONT Ports: 8 Expert Answers on Multicast, QoS & Buffer Specs
2026-10-27 09:21:35
Popular Posts
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Mitigating Broadcast Storms
2026-06-22 15:50:47
Access Control List (ACL) Hardware TCAM Resource Allocation Guidelines - Official Technical Overview & Hardware Datasheet
2026-09-30 11:01:02
Managing OEM ONT: Initial Setup, Console Connection & Firmware Upgrades FAQ
2026-10-15 17:10:22
Random Posts
Merchant Silicon vs Custom ASIC Switches: A Data-Driven Performance Evaluation of Throughput, Latency, and TCO
2026-06-03 14:11:13
Enterprise VPN Gateway Router Buy - Carrier-Grade Routing Solution Brief: Deploying Enterprise VPN Gateway Router Buy
2026-05-25 15:21:00
IEEE & MEF Compliance Masterclass: Advanced Protocol Handling of Can an OEM ONT synchronize with an OLT operating on an external BITS clock reference?
2026-10-22 10:31:33
Recent Posts
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
2026-10-30 11:30:33
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
2026-10-30 10:06:06
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
2026-10-30 10:03:46
About
XponShop blog describes some basics for Huawei / ZTE /
Nokia / FiberHome GPON OLT, ONT, SFP, and Site Power...
such as configurations, issue troubleshooting, knowledge
sharing, and keeps updating.
Recent posts
 AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
 Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
 Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
Products from the blog
CORE SECURITY POSITIONING
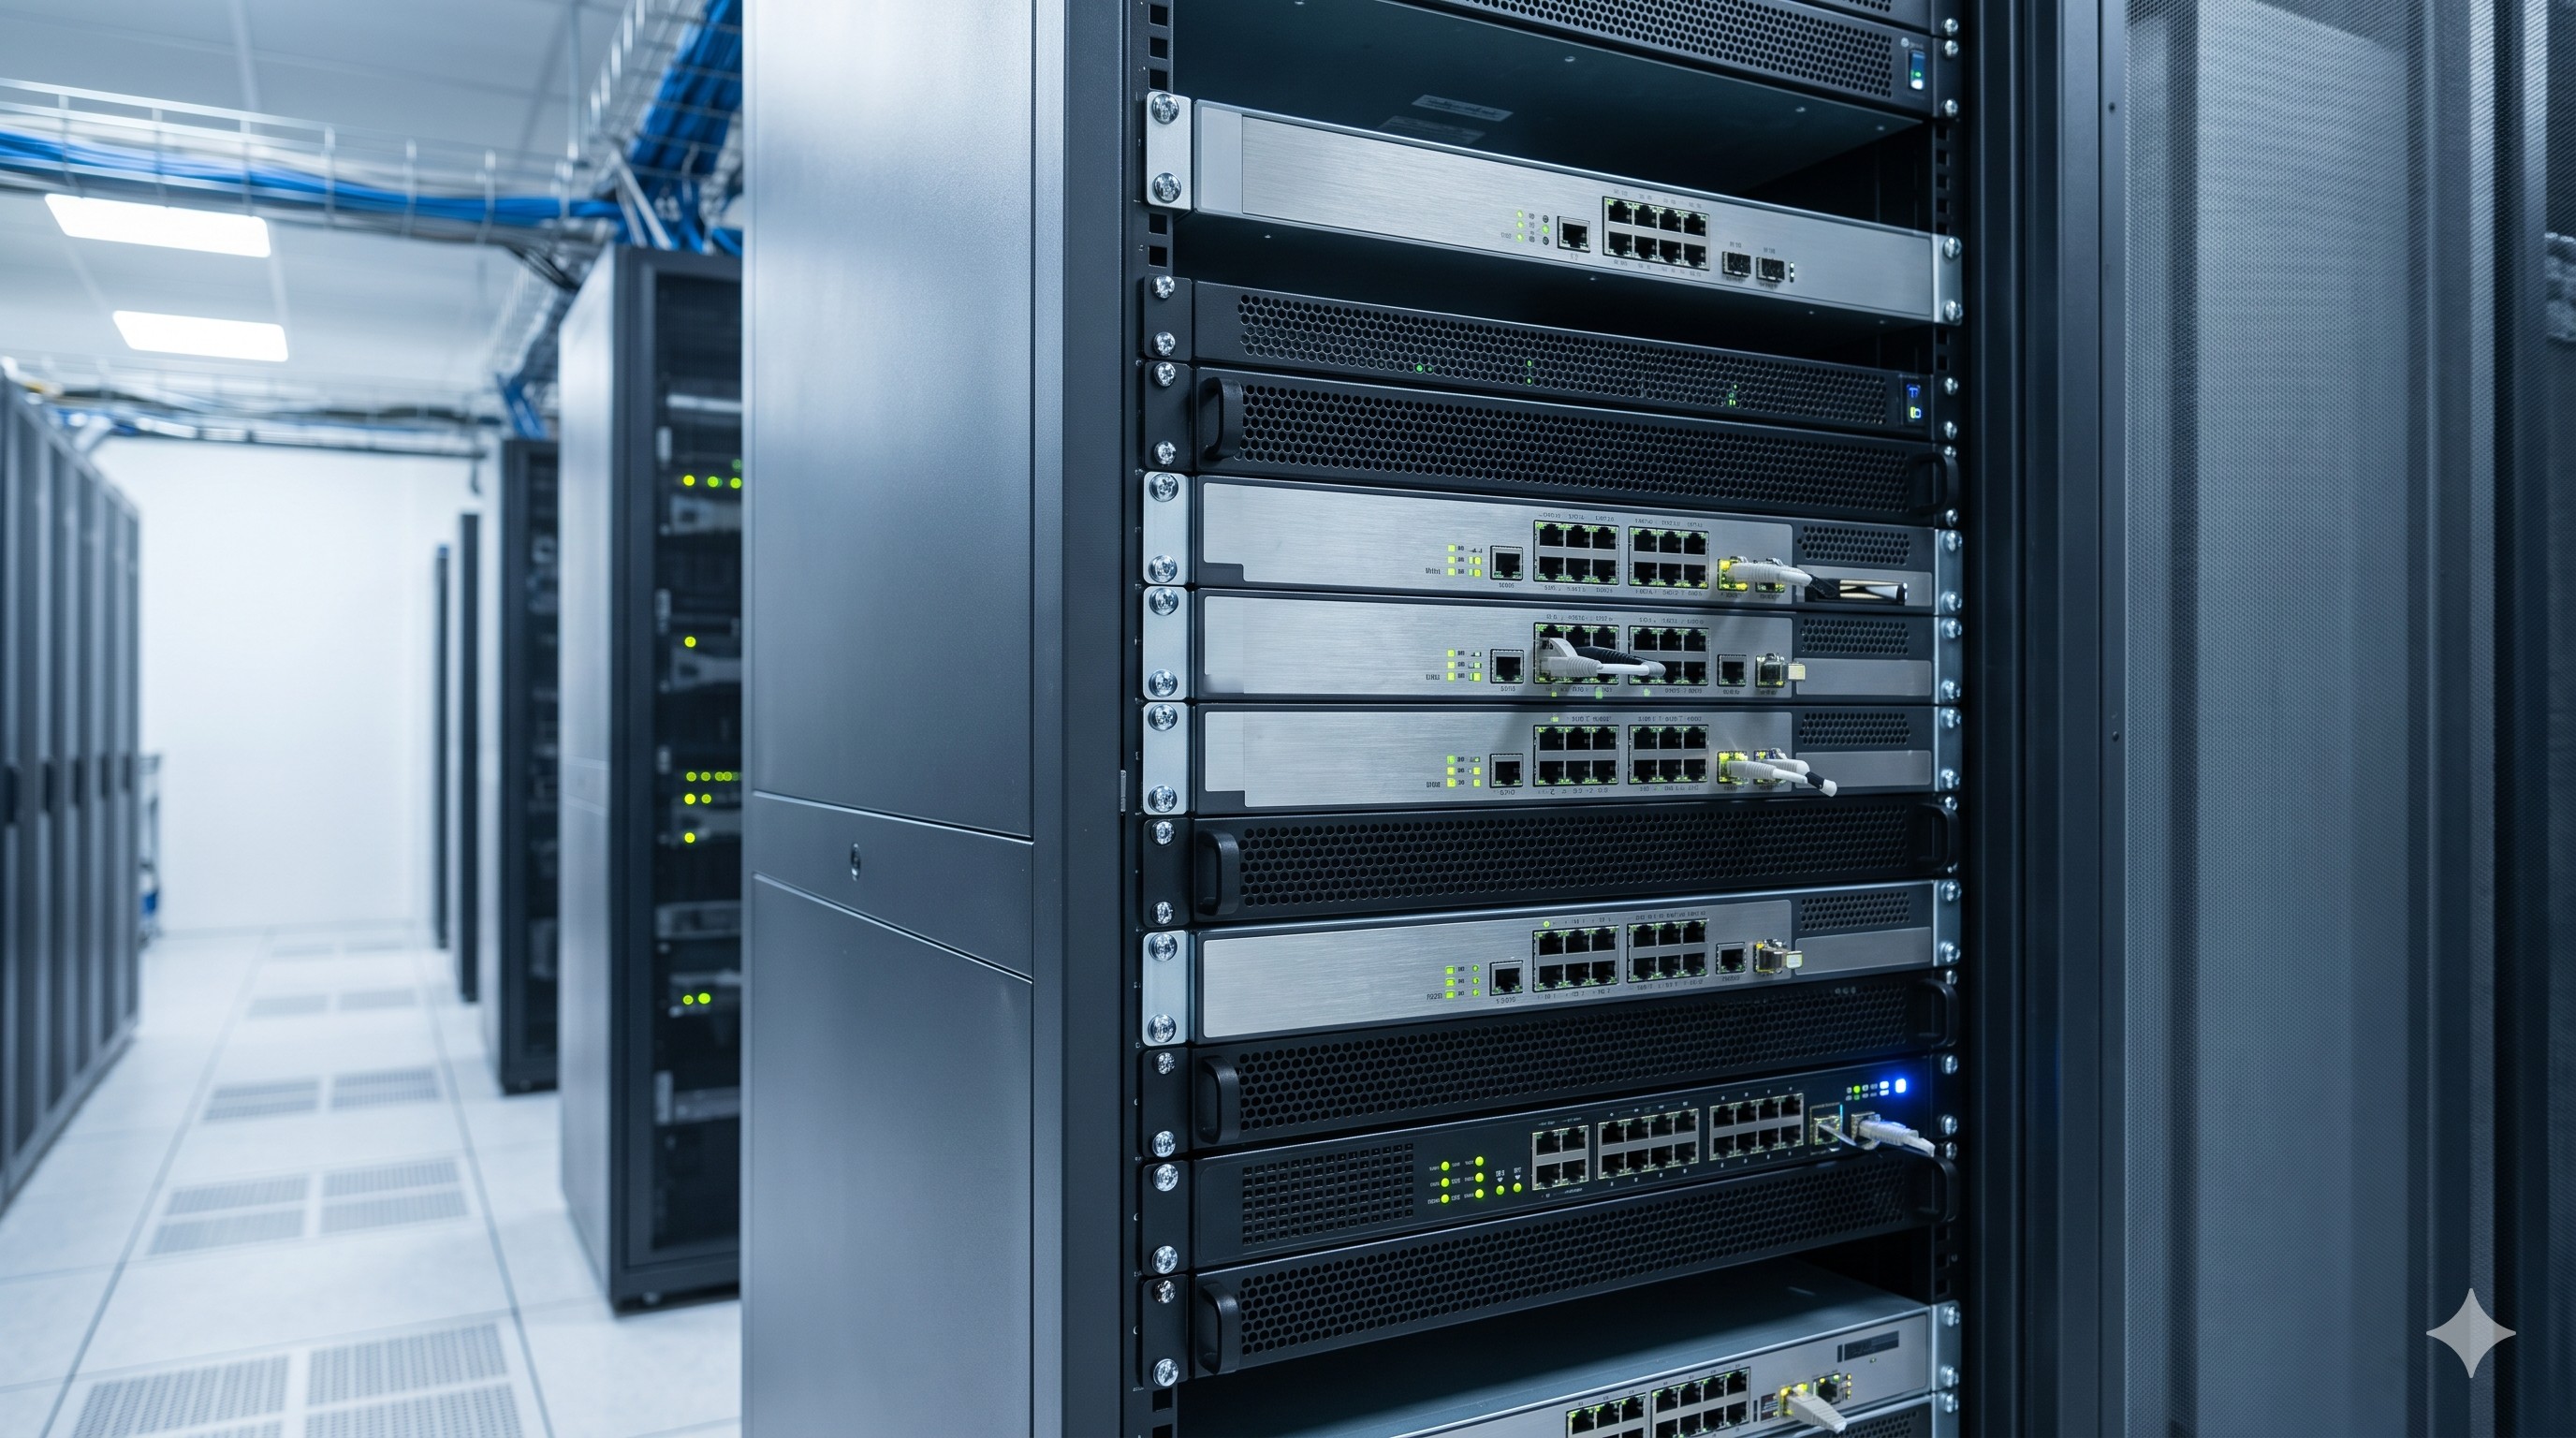
This document serves as the definitive technical reference and product datasheet for the Secured Routing Platform, a next-generation edge gateway router engineered to establish a new benchmark for network infrastructure security, performance, and operational resilience. Designed for the demanding environments of enterprise campuses, carrier points of presence, and distributed branch locations, this platform delivers integrated, hardware-accelerated security without compromising line-rate forwarding performance. It represents a strategic evolution in edge routing, moving beyond traditional perimeter defense to embed security at the very core of the data plane.
HARDWARE MACSEC CAPABILITIES
The cornerstone of the platform's security architecture is its comprehensive, hardware-accelerated implementation of IEEE 802.1AE (MACsec). This is not a software overlay but a deeply integrated function within the packet forwarding ASIC, enabling wire-speed encryption and decryption for all traffic traversing the interface. By securing data at Layer 2, the platform provides robust protection against man-in-the-middle attacks, eavesdropping, and other physical-layer vulnerabilities across the entire network fabric.
- **Line-Rate MACsec Encryption:** The dedicated hardware engine supports 256-bit encryption keys, ensuring data confidentiality and integrity at speeds matching the platform's full switching capacity. This eliminates the performance penalty typically associated with software-based encryption solutions.
- **Flexible Key Agreement:** Full support for the MACsec Key Agreement (MKA) protocol (IEEE 802.1X-2010) allows for dynamic, centralized key management and distribution. This integrates seamlessly with existing RADIUS and AAA infrastructures, providing policy-based access control and automated key rotation.
- **Comprehensive Interface Support:** MACsec is available across a wide range of physical interface types, including Gigabit Ethernet (RJ45) and Fiber (SFP/SFP+), ensuring security can be enforced on both copper and optical links throughout the network.
- **Multi-level Security:** The implementation supports both static (pre-shared key) and dynamic (MKA) operation modes, providing deployment flexibility to match operational requirements.
PHYSICAL INTERFACE ISOLATION
Beyond cryptographic security, the platform incorporates advanced physical isolation mechanisms to safeguard the integrity of the hardware and the network. These measures are critical for multi-tenant environments and for preventing accidental or malicious misconfiguration.
- **Hardware-Based Line Card Isolation:** Each line card and its associated interfaces are logically and electrically isolated at the hardware level. This prevents a failure or security compromise on one port from impacting traffic or control plane operation on other ports.
- **Secure Management Plane:** A dedicated management Ethernet port and an out-of-band (OOB) serial console port provide physically separated access for system administration. This management plane can be entirely firewalled from the data plane, ensuring administrative access remains available even during network anomalies.
- **Hardware Root of Trust (e.g., TPM):** The platform incorporates a dedicated security co-processor (Trusted Platform Module) to establish a hardware root of trust. This secures the boot process, verifies the integrity of the system firmware and OS image, and provides secure storage for cryptographic keys and certificates, preventing unauthorized software execution and platform tampering.
- **Discrete Port Disablement:** Individual physical interfaces can be administratively disabled at the hardware level, providing a mechanism to shut down compromised or unused ports to prevent unauthorized physical access.
DETAILED PARAMETERS
TECHNICAL SPECIFICATIONS
The following table details the key hardware and performance parameters for the Secured Routing Platform.
TELECOM CERTIFICATIONS
To ensure reliable operation within diverse and demanding telecommunications environments, the Secured Routing Platform has been rigorously tested and certified against a comprehensive suite of industry standards.
- **Safety:** UL 60950-1 / CSA C22.2 No. 60950-1, EN 60950-1, IEC 60950-1, and the updated EN 62368-1 for Audio/Video, Information and Communication Technology Equipment.
- **EMC:** FCC Part 15 (Class A), EN 55032 (Class A), EN 55024, CISPR 32, and VCCI for EMC compliance.
- **Environmental:** NEBS GR-63-CORE and NEBS GR-1089-CORE (Level 3), ensuring resilience to environmental stress such as temperature extremes, humidity, vibration, and electromagnetic interference.
- **Regulatory:** RoHS and WEEE compliance for environmental sustainability.
- **Carrier Ethernet:** MEF 9, MEF 14, and MEF 26 certified, confirming compliance with Carrier Ethernet service definitions, performance metrics, and management standards.
- **Security:** FIPS 140-2 validated cryptographic module (pending), providing assurance on the strength and integrity of the implemented cryptographic algorithms.
SECURED TOPOLOGY
The Secured Routing Platform is ideally positioned as a high-performance, security-centric gateway at the edge of enterprise campus networks, between a trusted internal infrastructure and untrusted external networks (e.g., WAN or internet). In a typical deployment, the platform connects to multiple internal distribution switches via high-speed fiber uplinks using secured MACsec connections. Multiple routers can be deployed in an active/active or active/standby configuration using VRRP or similar protocols for high availability. A dedicated management network provides secure out-of-band access for administration and monitoring. This architecture ensures that all inter-site and external traffic is cryptographically isolated and integrity-checked at the network boundary, delivering unmatched security and performance.
📥 Download Technical Specification
Click the button below to view or download the full official PDF datasheet.
⬇️ Download Official PDF