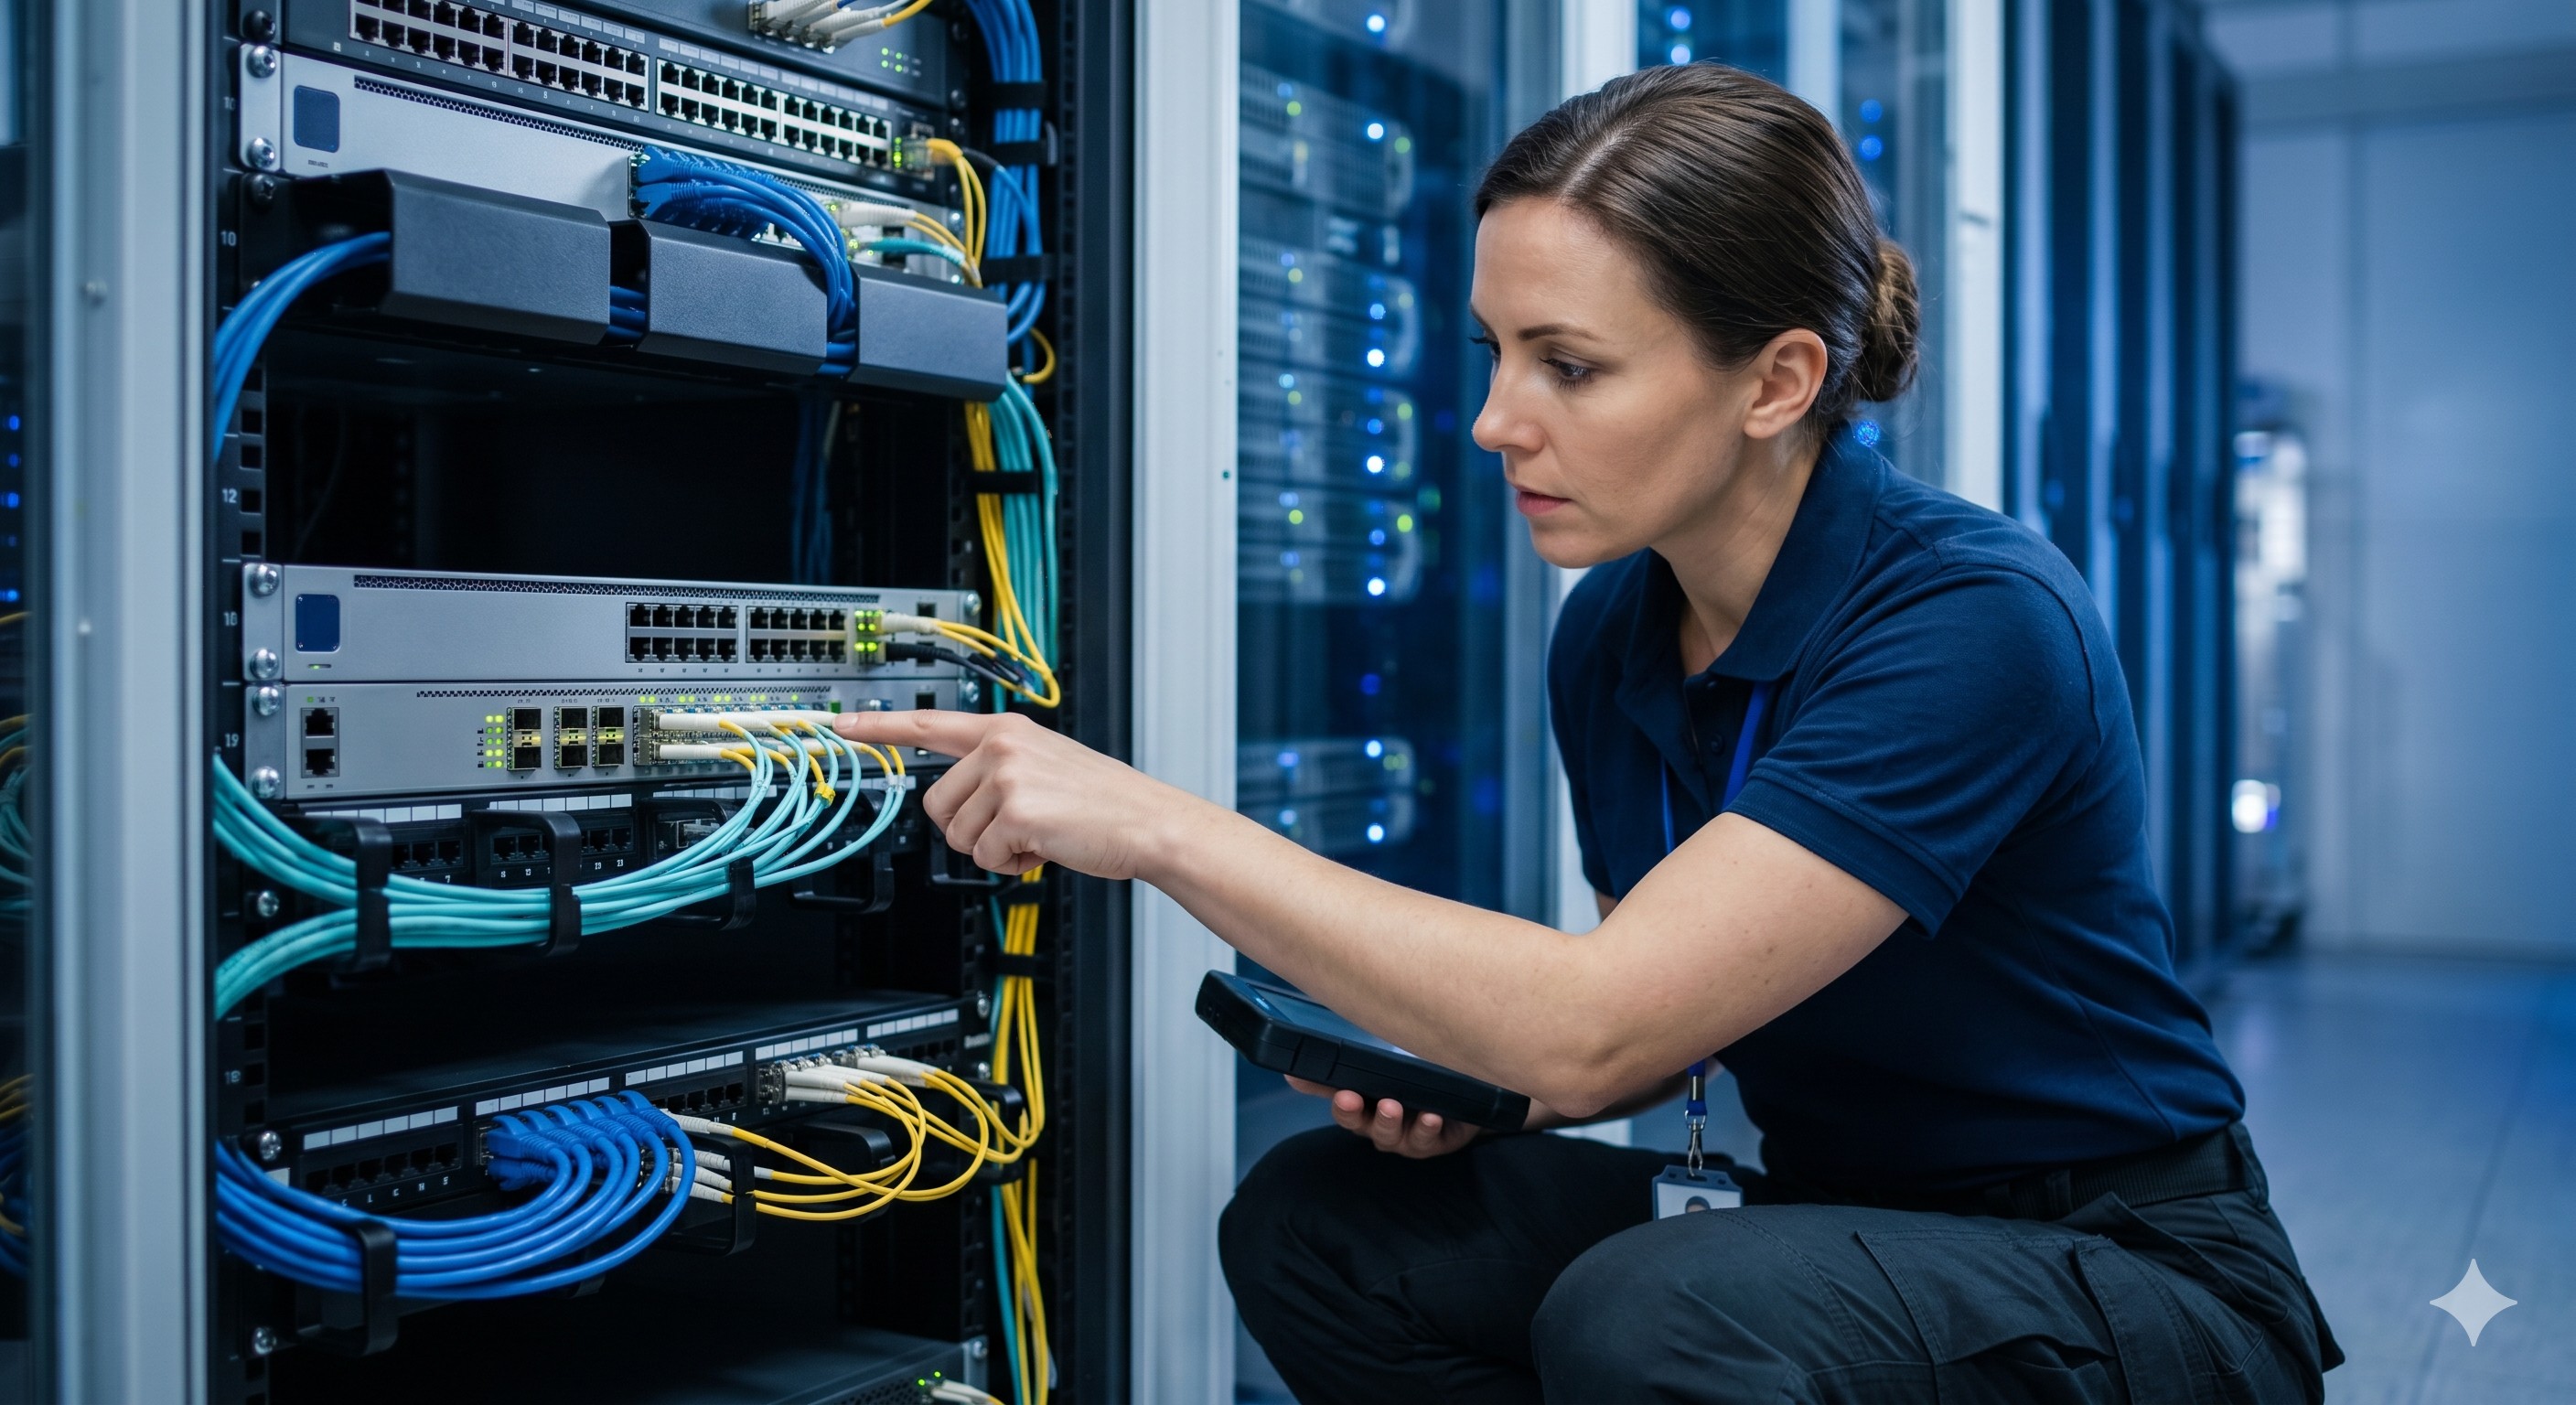
 Technical Support FAQ: Everything Network Architects Ask About Enterprise Router Configuration
04 Jun, 2026. Posted by:XPONSHOP
Most Views Posts
The Ultimate Guide to End-of-Sale (EOS) Announcements: Architecture, Backplane Bandwidth, and Deployment
2026-07-01 13:56:22
High-Density Fiber Infrastructure Application Note: Next-Generation 10G Symmetry: XGS-PON OLT Deployment Architecture Whitepaper
2026-09-16 11:32:35
Troubleshooting Cisco Switches: Optical Interfaces, Stacking Errors & Transceiver Compatibility
2026-08-03 10:11:37
XPONSHOP OEM GPON-to-XGS-PON Coexistence Splitter Insertion Loss Reference - Official Technical Overview & Hardware Datasheet
2026-09-07 10:17:57
Troubleshooting IEEE 802.1X: Optical Interfaces, Stacking Errors & L3 Protocols
2026-05-29 16:03:52
Popular Posts
Troubleshooting Rogue ONU Interference: Optical Interfaces, Stacking Errors & L3 Protocols FAQ
2026-09-28 10:10:10
The Ultimate Guide to 10G Ethernet Ports on ONUs: Architecture, Backplane Bandwidth, and Deployment
2026-09-09 10:40:46
Generic NMS FAQ: Expert Answers to Network Integration & Configuration Questions
2026-07-29 09:59:40
Random Posts
FiberHome AN5516-01 Large-Scale OLT Platform - Official Technical Overview & Hardware Datasheet
2026-06-25 14:35:35
High-Quality Chinese OEM Dual-Mode XPON ONU Hardware Selection Matrix - Official Technical Overview & Hardware Datasheet
2026-07-03 10:33:48
Layer 2 Broadcast Storm Suppression Configuration on Enterprise Switches - Official Technical Overview & Hardware Datasheet
2026-08-21 10:43:52
Managing ONT: Initial Setup, Console Connection & Firmware Upgrades FAQ
2026-10-28 09:33:13
Recent Posts
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
2026-10-30 11:30:33
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
2026-10-30 10:06:06
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
2026-10-30 10:03:46
About
XponShop blog describes some basics for Huawei / ZTE /
Nokia / FiberHome GPON OLT, ONT, SFP, and Site Power...
such as configurations, issue troubleshooting, knowledge
sharing, and keeps updating.
Recent posts
 AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
 Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
 Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
Products from the blog
Overview
Configuring an enterprise-class router requires precise attention to hardware specifications, protocol behavior, and redundancy mechanisms. This FAQ addresses both pre-sales architectural questions and post-sales CLI-level configuration issues, helping network engineers deploy carrier-grade routing infrastructure with minimal downtime.
Frequently Asked Questions