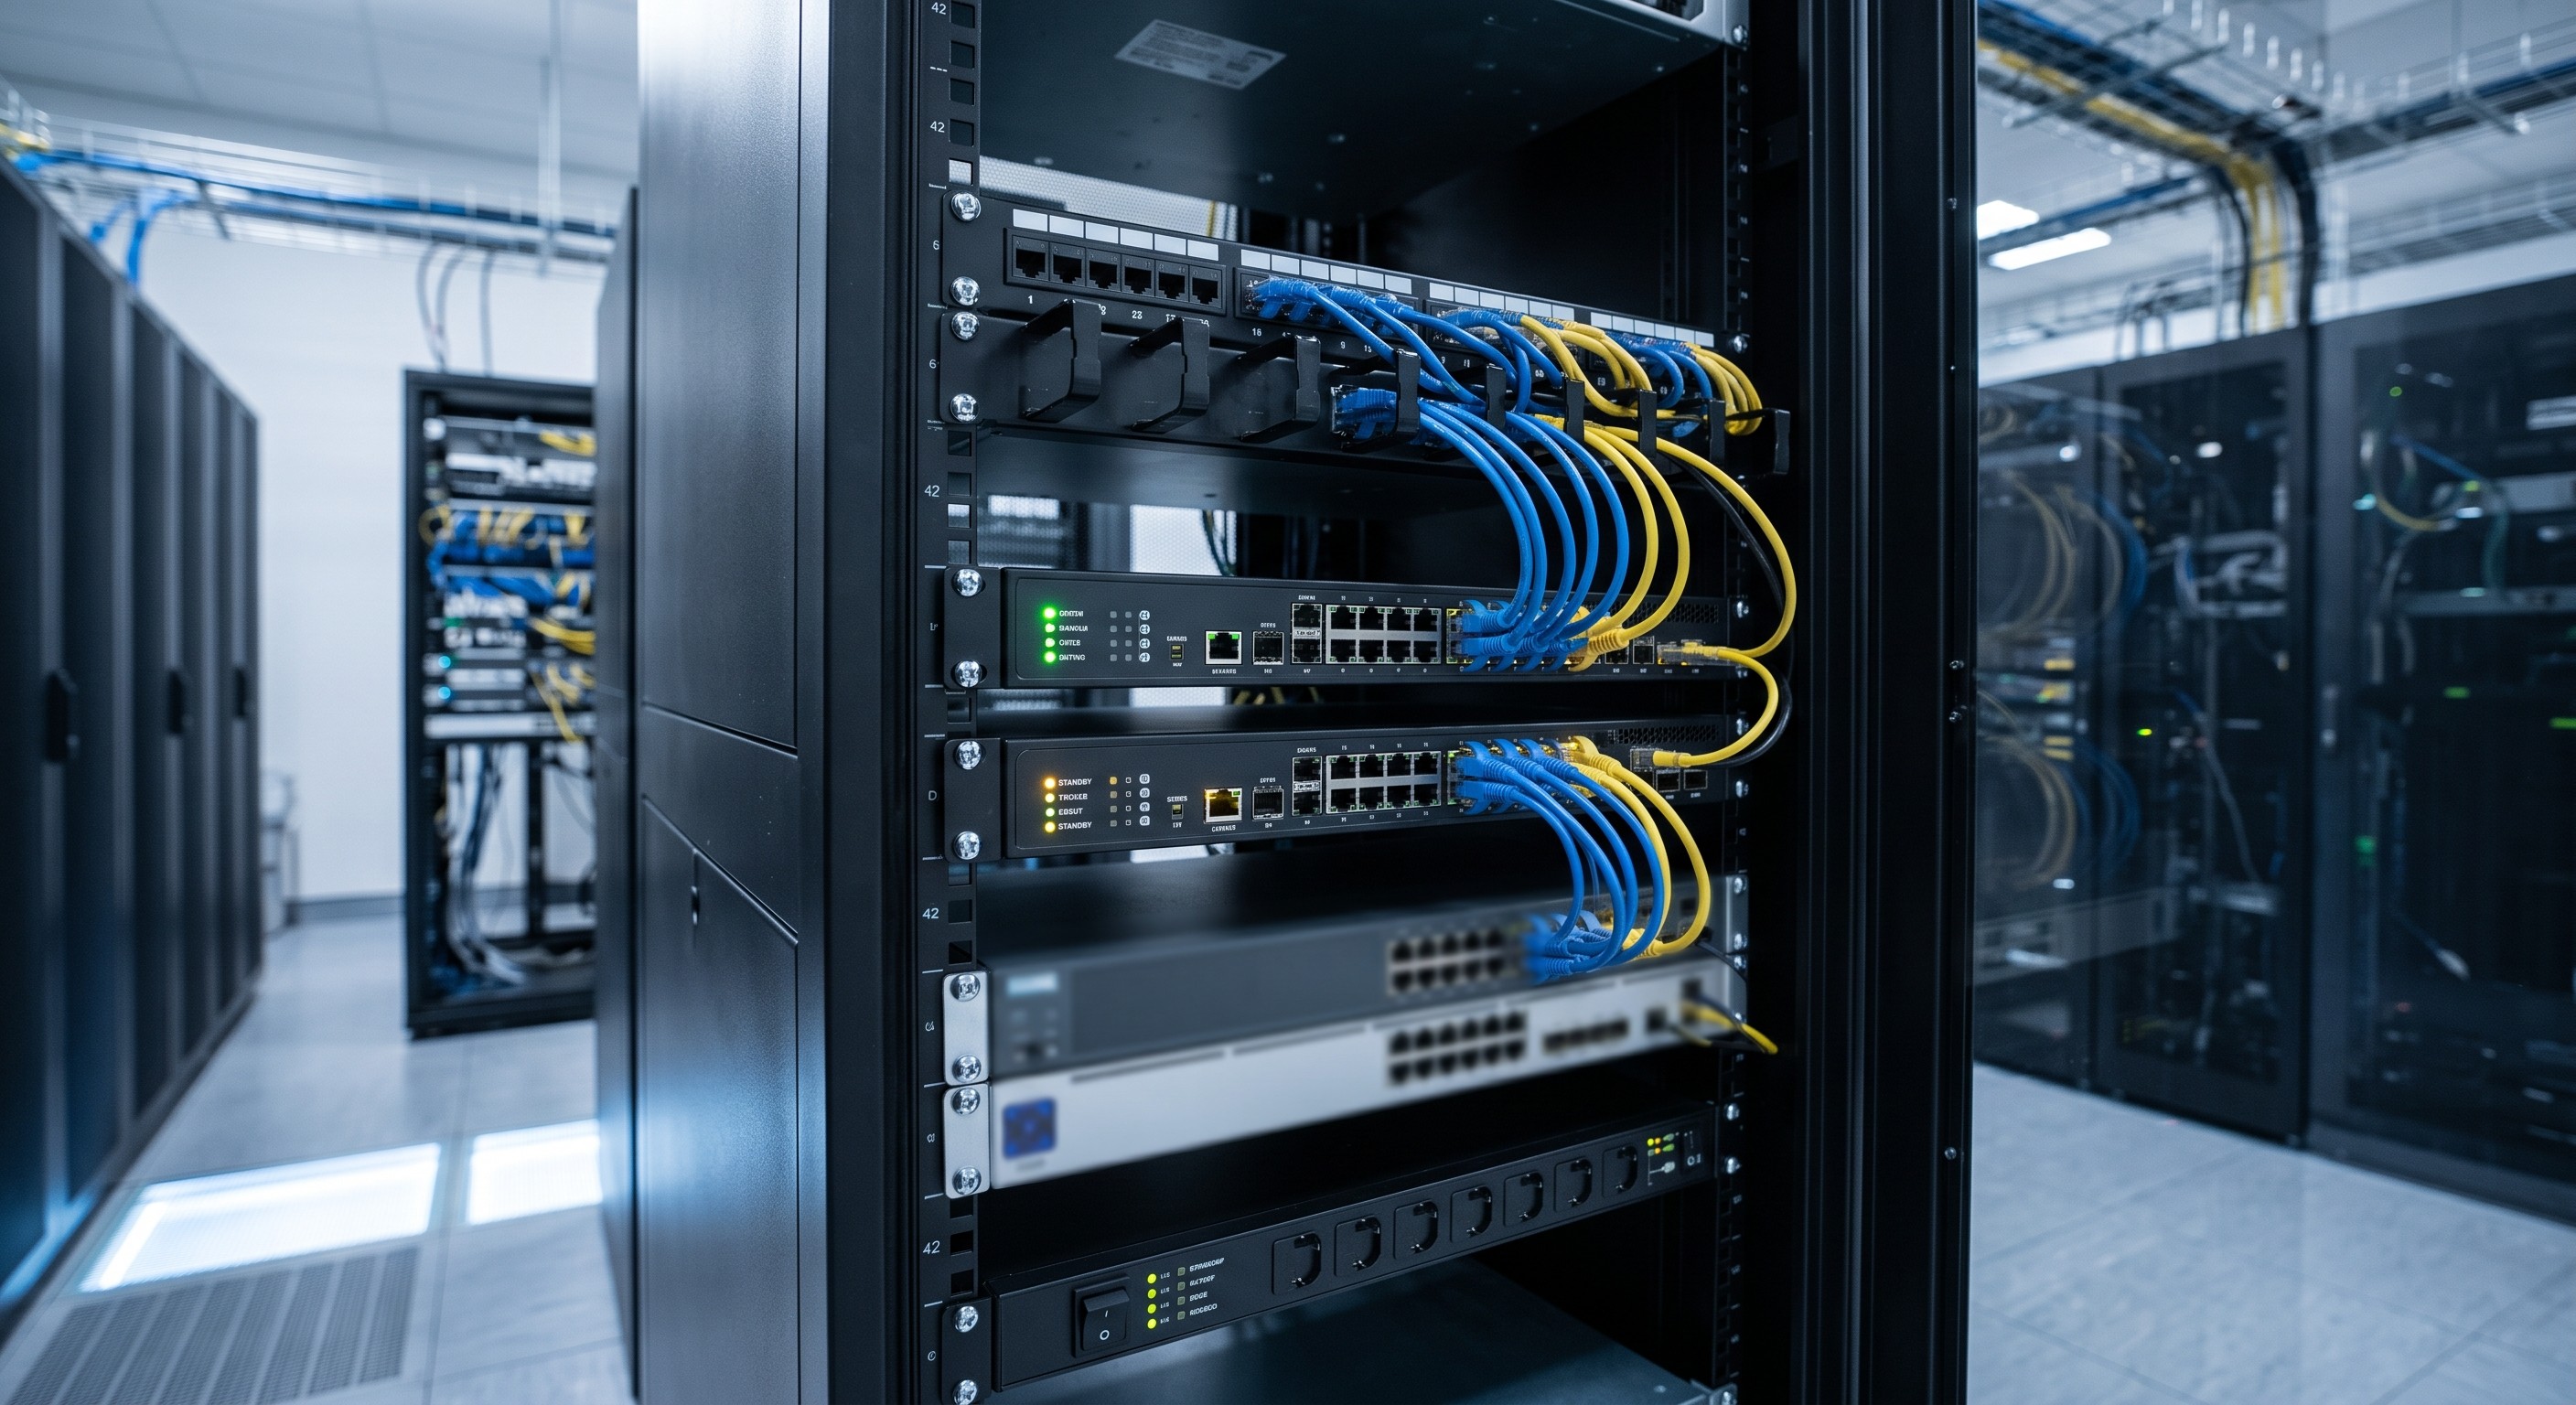
 Enterprise Core Systems Engineering Reference Manual: Enterprise Firewall High-Availability Clustering (Active/Standby) Configuration Blueprint
23 Sep, 2026. Posted by:XPONSHOP
Most Views Posts
Ultra-Low Latency Packet Buffering Engine Factsheet: Packet Buffer Memory Size Allocation
2026-05-28 16:05:11
In-Depth Architecture of the FiberHome AN5516-01 and AN5116-06B OLT 19-inch Chassis
2026-04-09 10:22:02
The Ultimate Guide to Telecom Regulatory Compliance: Architecture, Backplane Bandwidth, and Global Deployment
2026-09-01 11:03:19
The Definitive Guide to the ZTE ZXD1500 Rectifier in Telecom Power Systems
2026-03-06 10:59:03
Popular Posts
Maximizing Core Network ROI: A Total Cost of Ownership Analysis of Modular Architecture Switch Price
2026-05-25 15:06:12
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
2026-10-30 11:30:33
What Causes Network Loopback Storm - Official Technical Overview & Hardware Datasheet
2026-06-05 16:37:28
Random Posts
Common FAQs About Huawei MA5800 OLT
2025-10-22 08:47:02
XPONSHOP Alternative SFP-GIG-LX Optical Transceiver Temperature Range Verification - Official Technical Overview & Hardware Datasheet
2026-09-08 10:49:34
Carrier-Grade Routing Solution Brief: Deploying evolution of 100G to 400G network routing
2026-06-18 14:05:43
GPON ONT Management Ways: OMCI, TR069, U2000 or XML?
2025-10-22 09:04:07
Recent Posts
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
2026-10-30 11:30:33
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
2026-10-30 10:06:06
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
2026-10-30 10:03:46
About
XponShop blog describes some basics for Huawei / ZTE /
Nokia / FiberHome GPON OLT, ONT, SFP, and Site Power...
such as configurations, issue troubleshooting, knowledge
sharing, and keeps updating.
Recent posts
 AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
 Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
 Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
Products from the blog
PRODUCT IDENTIFICATION
The Enterprise Firewall High-Availability Clustering (Active/Standby) Configuration Blueprint defines the authoritative engineering standard for deploying carrier-class perimeter security at scale. This reference manual specifies the physical chassis, failover control plane, and synchronization fabric required to achieve sub-second convergence between an Active and Standby security appliance pair. Designed for Tier-1 datacenters, financial exchange perimeters, and multi-tenant service provider edge networks, the blueprint eliminates single points of failure across power, forwarding, and stateful inspection domains. Every parameter in this document reflects validated OEM interoperability criteria for enterprise firewall clustering in Active/Standby topology.
CORE INTERNAL TOPOLOGY
The Active/Standby clustering architecture is built upon a dedicated High-Availability (HA) control plane that operates independently of the primary data forwarding path. Each firewall node contains a dual-stage failover engine: a heartbeat subsystem for liveness detection and a state synchronization pipeline for connection table mirroring. The heartbeat subsystem utilizes redundant dedicated HA interfaces with configurable hello and hold timers, while the synchronization pipeline employs deterministic session replication for TCP, UDP, ICMP, and application-layer stateful inspection contexts.
The internal topology consists of three logical planes:
1. DATA PLANE - Line-rate packet forwarding and deep packet inspection ASICs operating in Active or Standby mode.
2. CONTROL PLANE - HA election state machine, priority arbitration, and preemption logic.
3. SYNCHRONIZATION PLANE - Encrypted stateful failover channel carrying session tables, NAT mappings, VPN security associations, and dynamic routing adjacencies.
Upon primary node failure, the Standby node transitions to Active within the configured failover threshold, preserving all synchronized sessions and maintaining uninterrupted service delivery.
SWITCHING SUBSYSTEM CAPABILITIES
The firewall clustering blueprint supports multiple HA deployment modes to accommodate diverse network topologies. Active/Standby mode delivers a one-to-one redundancy model where the Standby appliance maintains full session state without forwarding production traffic. The subsystem supports the following operational capabilities:
- Stateful Failover: Full session table synchronization including TCP state, UDP pseudo-state, ICMP, and application layer gateways (ALG).
- Asymmetric Routing Support: HA pair maintains synchronized routing tables to prevent path asymmetry failures.
- Link State Propagation: Physical interface failures on the Active node trigger immediate failover to the Standby node.
- HA Heartbeat Encryption: All synchronization traffic is protected using AES-256 encryption with pre-shared key or certificate-based authentication.
- Failover Threshold Configuration: Administrators may define heartbeat interval, hold timer, and failover trigger conditions.
- Preemption Control: Configurable preempt mode with delay timer to prevent flapping.
OPERATIONAL ADVANTAGES
Enterprise Firewall HA Clustering delivers measurable operational advantages for mission-critical network perimeters. The solution eliminates planned and unplanned downtime through transparent failover, reduces operational expenditure through centralized management of the HA pair, and ensures compliance with regulatory uptime mandates. Key operational advantages include:
- Sub-Second Failover: Validated failover times under 500 milliseconds for stateful session preservation.
- Zero Session Loss: Synchronized connection tables ensure no re-establishment of TCP sessions during failover.
- Simplified Management: Single management IP for the HA pair with unified policy deployment.
- Geographic Redundancy: HA pairs may be deployed across datacenter halls or availability zones with latency-tolerant heartbeat.
- Rolling Upgrades: Software updates may be applied to the Standby node first, followed by controlled failover, eliminating maintenance windows.
SPECIFICATION MATRIX
The following specification matrix defines the validated hardware and software parameters for the Enterprise Firewall High-Availability Clustering (Active/Standby) Configuration Blueprint. All values represent OEM-verified operating limits under standard enterprise deployment conditions.
REGULATORY COMPLIANCE
The Enterprise Firewall High-Availability Clustering blueprint complies with the following international standards and regulatory directives:
- Safety: IEC 60950-1, IEC 62368-1, UL 60950-1, EN 60950-1
- EMC: FCC Part 15 Subpart B Class A, EN 55032 Class A, EN 55024, VCCI Class A
- Environmental: RoHS 2011/65/EU, WEEE 2012/19/EU, REACH
- Telecom: NEBS Level 3 (GR-1089-CORE, GR-63-CORE) where applicable
- Security: Common Criteria EAL4+, FIPS 140-2 Level 2 validated cryptographic module
- Network Standards: IEEE 802.3, IEEE 802.1Q VLAN, IEEE 802.1AX Link Aggregation, IETF RFC 3768 VRRP, RFC 5798 VRRPv3
📥 Download Technical Specification
Click the button below to view or download the full official PDF datasheet.
⬇️ Download Official PDF