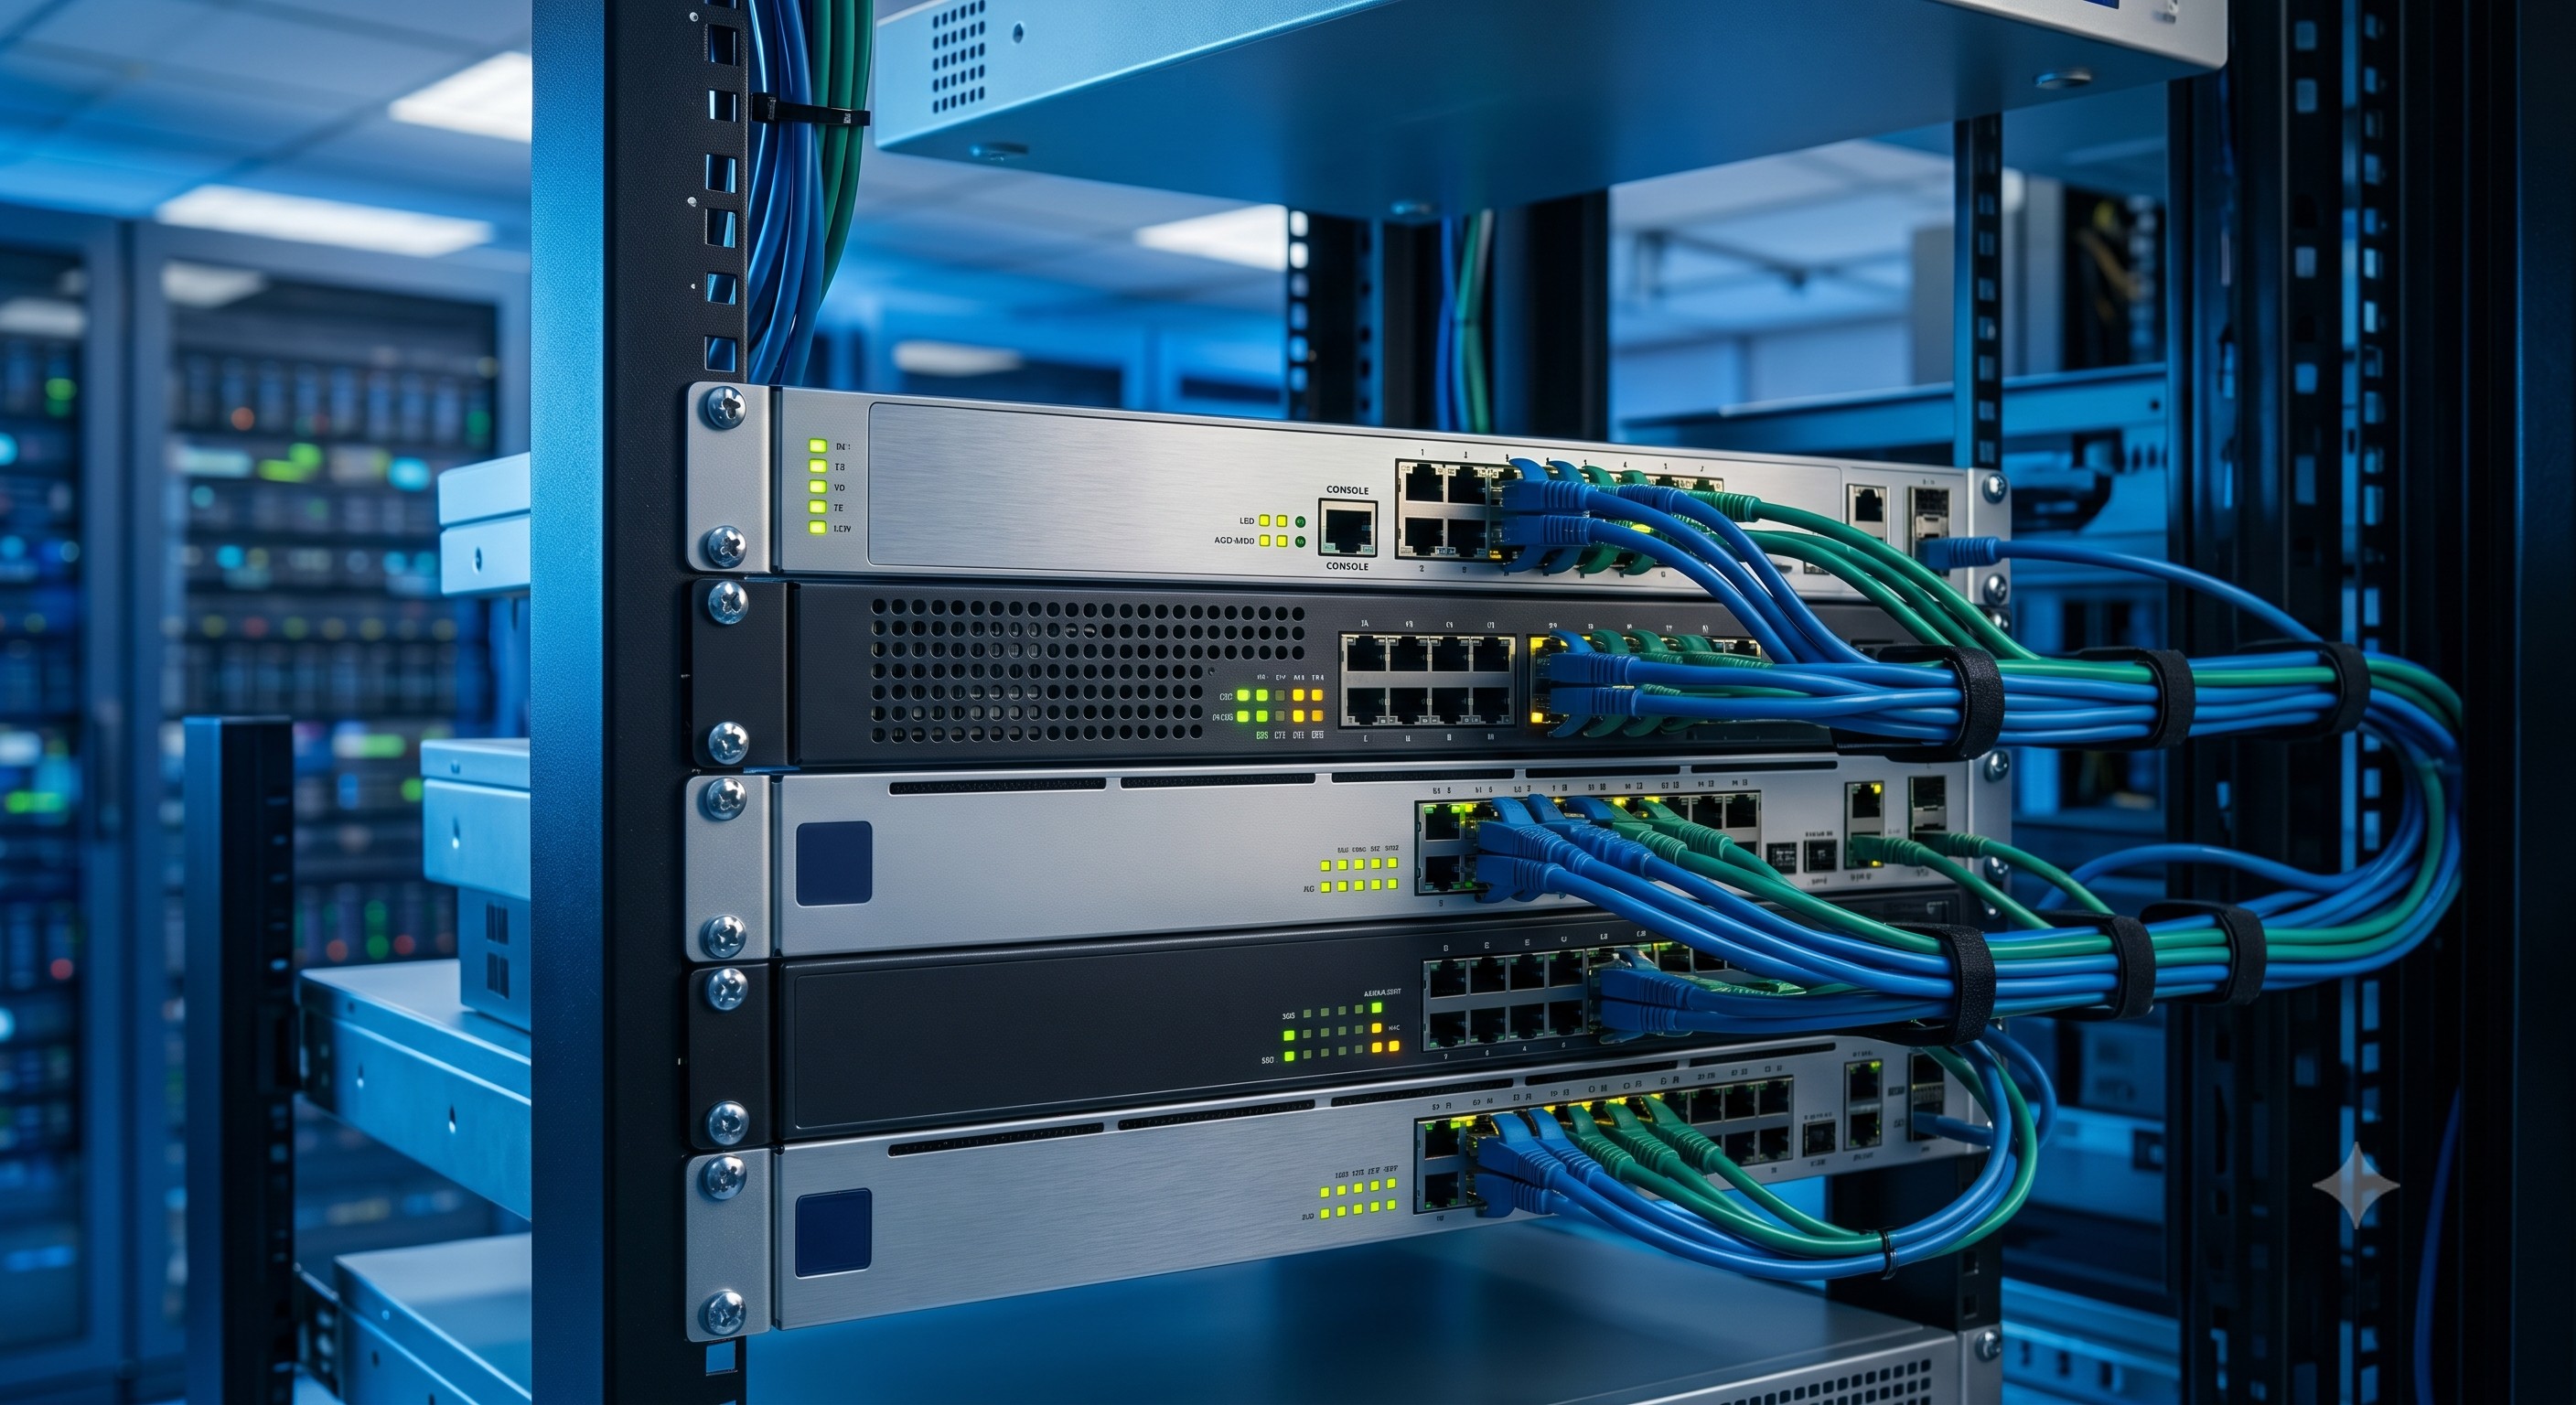
 Enterprise Core Systems Engineering Reference Manual: Safe Firmware Update Protocol for High-Availability Network Switches
08 Jun, 2026. Posted by:XPONSHOP
Most Views Posts
IP Address Conflict FAQ: Expert Answers for ONT Home Networks
2026-08-13 11:39:25
The Ultimate Guide to Broadband Remote Access Server (BRAS): Architecture, Backplane Bandwidth, and Deployment
2026-07-22 10:40:21
Managing ONT WAN: Initial Setup, Console Connection & Static IP Configuration FAQ
2026-10-08 11:31:49
Popular Posts
Overcoming Network Bottlenecks: Enterprise Configuration Manual for 160MHz Channel Bandwidth on Wi-Fi 6 ONT
2026-10-10 10:26:43
Port Isolation in Industrial Ethernet Switching - Official Technical Overview & Hardware Datasheet
2026-06-05 16:28:19
Maximizing Core Network ROI: A Total Cost of Ownership Analysis of OEM Fiber Hardware Sourcing
2026-07-06 14:03:12
The Ultimate Guide to End-of-Sale (EOS) Announcements: Architecture, Backplane Bandwidth, and Deployment
2026-07-01 13:56:22
Managing {keyword}: Initial Setup, Console Connection & Firmware Upgrades FAQ
2026-10-29 09:25:34
Random Posts
FiberHome AN5516-01 OLT 19inch Chassis Guide
2026-03-16 10:33:36
How to Configure the INTERNET WAN of Huawei ONT on MA5800-X17?
2025-10-22 09:00:39
Enterprise Core Systems Engineering Reference Manual: Automated Guided Vehicle (AGV) Wireless Roaming Router
2026-06-16 15:51:26
cloud-managed network router wholesale - Official Technical Overview & Hardware Datasheet
2026-05-26 13:46:11
Huawei MA5800 10G PON Solution
2025-10-22 08:48:51
Recent Posts
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
2026-10-30 11:30:33
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
2026-10-30 10:06:06
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
2026-10-30 10:03:46
About
XponShop blog describes some basics for Huawei / ZTE /
Nokia / FiberHome GPON OLT, ONT, SFP, and Site Power...
such as configurations, issue troubleshooting, knowledge
sharing, and keeps updating.
Recent posts
 AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
 Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
 Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
AI Optical Transceivers vs. Telecom Optical Transceivers: Two ‘Personalities’ of the Same Component
27 Mar, 2025
Overcoming Network Bottlenecks: Enterprise Configuration Manual for Nintendo Switch NAT Type D Resolution
27 Mar, 2025
Cisco Business 350 Series Managed Switch Physical Security and Power Efficiency - Official Technical Overview & Hardware Datasheet
27 Mar, 2025
Products from the blog
PRODUCT IDENTIFICATION
Document Number: TN-SFU-2026-01
Revision: 1.0
Product Family: SafeUpdate™ Firmware Management Subsystem for Carrier & Enterprise Switching Platforms
This document specifies the engineering requirements, hardware-assisted safety mechanisms, and validated operational procedures for performing zero-downtime, non-disruptive firmware updates on mission-critical network switching infrastructure. The SafeUpdate™ protocol integrates hardware-level rollback protection, dual-image atomic commits, and pre-validation logic to eliminate update-related service outages.
CORE INTERNAL TOPOLOGY
The SafeUpdate™ architecture leverages a partitioned Flash memory subsystem comprising two physically isolated boot banks (Bank A and Bank B), a hardware watchdog timer (WDT) with independent clock source, and a BMC (Baseboard Management Controller) that supervises the update transaction. A CRC-32 checksum engine validates firmware integrity prior to committing the boot flag. The switching ASIC remains fully operational in pass-through mode during image writing, facilitated by a zero-downtime restart mechanism for control plane processes.
Key Hardware Components:
- Dual-redundant SPI NOR Flash (≥512 Mbit each)
- Hardware monotonic update counter (prevents rollback to vulnerable versions)
- OOB (Out-Of-Band) management port for recovery image loading
- Power-fail protection capacitor bank (holds write cycles for >30ms during brownout)
SWITCHING SUBSYSTEM CAPABILITIES
- Atomic Image Commit: New firmware is written to inactive bank while active bank continues switching. A final confirmation triggers bank-swap and warm reboot (sub-50ms data plane disruption).
- Silent Validation: Hash verification (SHA-256) and signature check (RSA-2048) occur before boot flag modification. Corrupted images are automatically rejected.
- Automated Fallback: If new image fails to boot three consecutive times, WDT triggers revert to last-known-good bank without operator intervention.
- Telemetry Logging: Every update attempt is recorded in non-volatile system journal (syslog, timestamp, image version, outcome).
OPERATIONAL ADVANTAGES
- Zero Packet Loss for L2/L3 forwarding during image write phase (control plane isolated)
- <5-second total service restoration for management interfaces (SSH/SNMP/WebUI)
- Supports ISSU (In-Service Software Upgrade) for compatible dual-supervisor chassis
- Remote update capability via IPv4/IPv6 management VLAN (TLS 1.3 encrypted)
TECHNICAL SPECIFICATIONS
Firmware Format: .bin or .pkg, signed with vendor certificate
Compatible File Systems: FAT32, EXT4 (USB), TFTPv2, FTP, SFTP
Update Trigger Methods: CLI (console/SSH), SNMPv3, RESTCONF, USB AutoUpdate
Maximum Image Size: 256 MB (expandable to 1 GB via external USB)
Update Transaction Log: 1024 entries stored in FRAM (retention 10 years)
Environmental Operating Range: 0°C to 50°C during update process
Certified Protocols for Transfer: TFTP Block Size 8192 bytes, TCP window scaling for FTP/SFTP
REGULATORY COMPLIANCE
- IEC 62443-4-1 Secure product development lifecycle (update integrity)
- NIST SP 800-147 BIOS protection guidelines (hardware root-of-trust)
- Common Criteria EAL2+ for firmware load mechanisms
- RoHS 3 (2015/863/EU) – no hazardous substances in storage media
- REACH SVHC compliant
DEPLOYMENT NOTES
- Always verify digital signature before initiating update: `show firmware signature`
- Confirm active/inactive bank status: `show boot bank`
- For dual-supervisor chassis, maintain SSO (Stateful Switchover) capability during ISSU
- Recommended backup image retention: minimum 2 previous stable releases
- Update window for rolling back: maximum 10 minutes (after which new image is marked ‘committed’ and old bank may be overwritten)
SAFEUPDATE™ ENGINEERING BEST PRACTICES
1. Pre-update validation: Verify power redundancy (PSU A & B online), temperature within spec, CPU load <70%.
2. Perform update during maintenance window via out-of-band console session.
3. Use `update check` command to run compatibility pre-scan.
4. After warm reboot, confirm data plane stability with `show interface counters errors`.
5. If ISSU fails, automatic rollback occurs; manual intervention via `boot bank [0|1]` from console.
SUPPORTED PLATFORM MATRIX
All switching platforms carrying the SafeUpdate™ hardware stamp (models S-Series 5000, 7000, 9000; E-Series edge switches; C-Series campus cores) support the full feature set described herein. Contact technical support for legacy platform upgrade compatibility. Maximum supported firmware versions: 5.x and later.
📥 Download Technical Specification
Click the button below to view or download the full official PDF datasheet.
⬇️ Download Official PDF